Key takeaway: Secure by Design is the core concept of QNAP's product development process
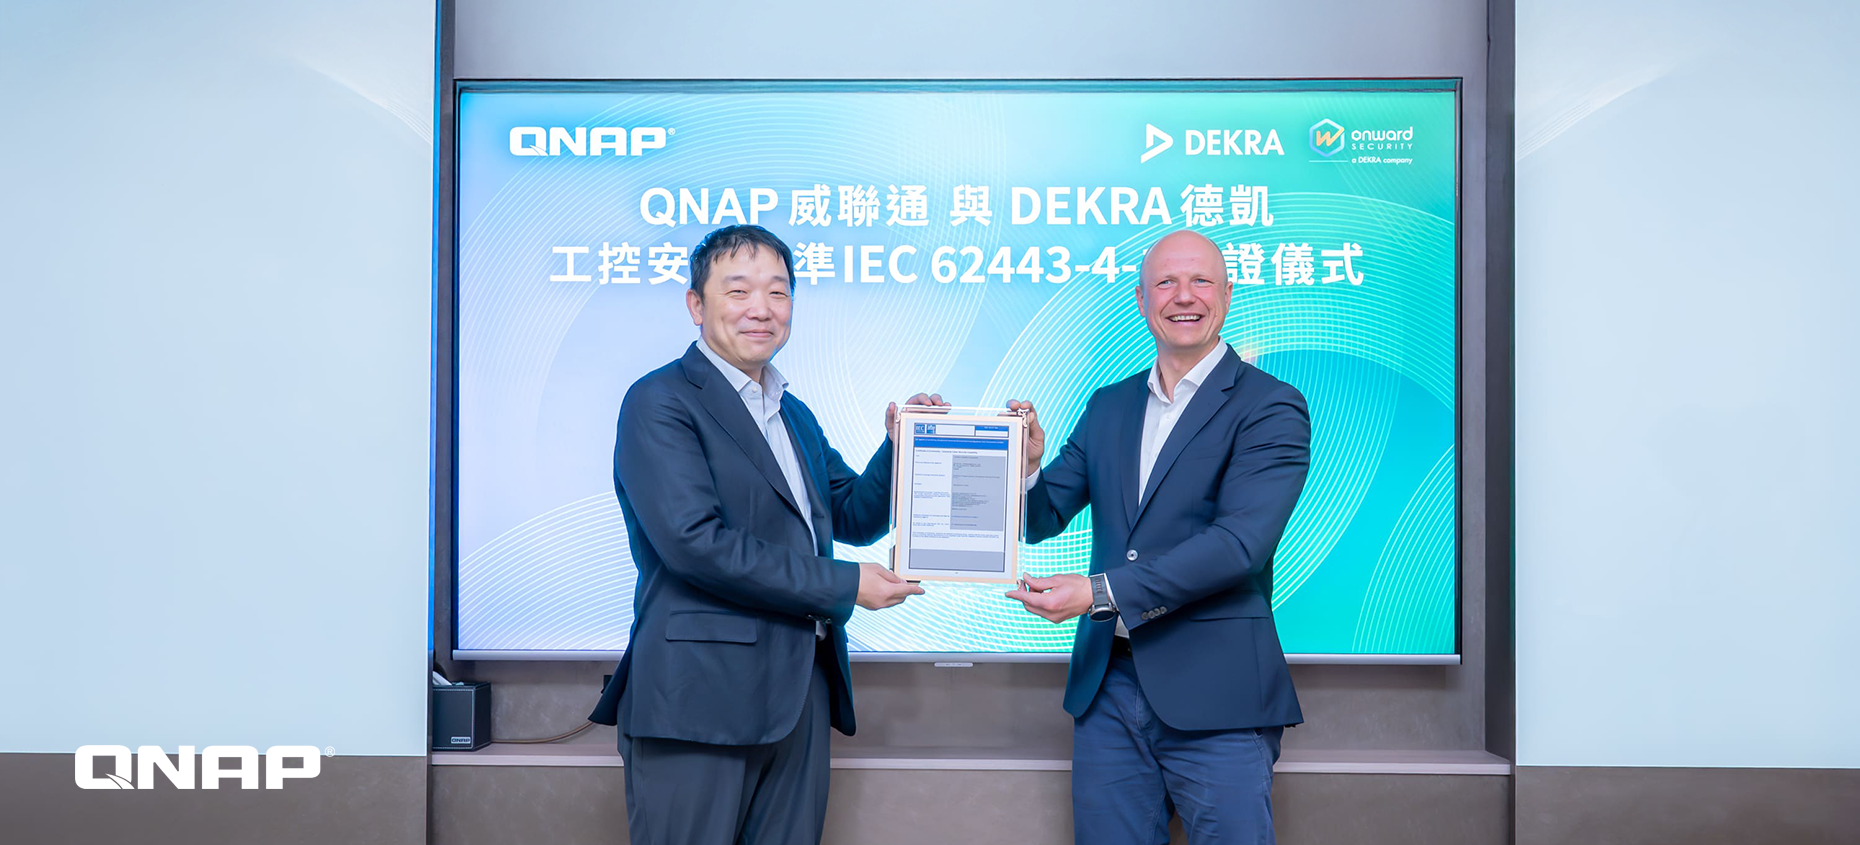
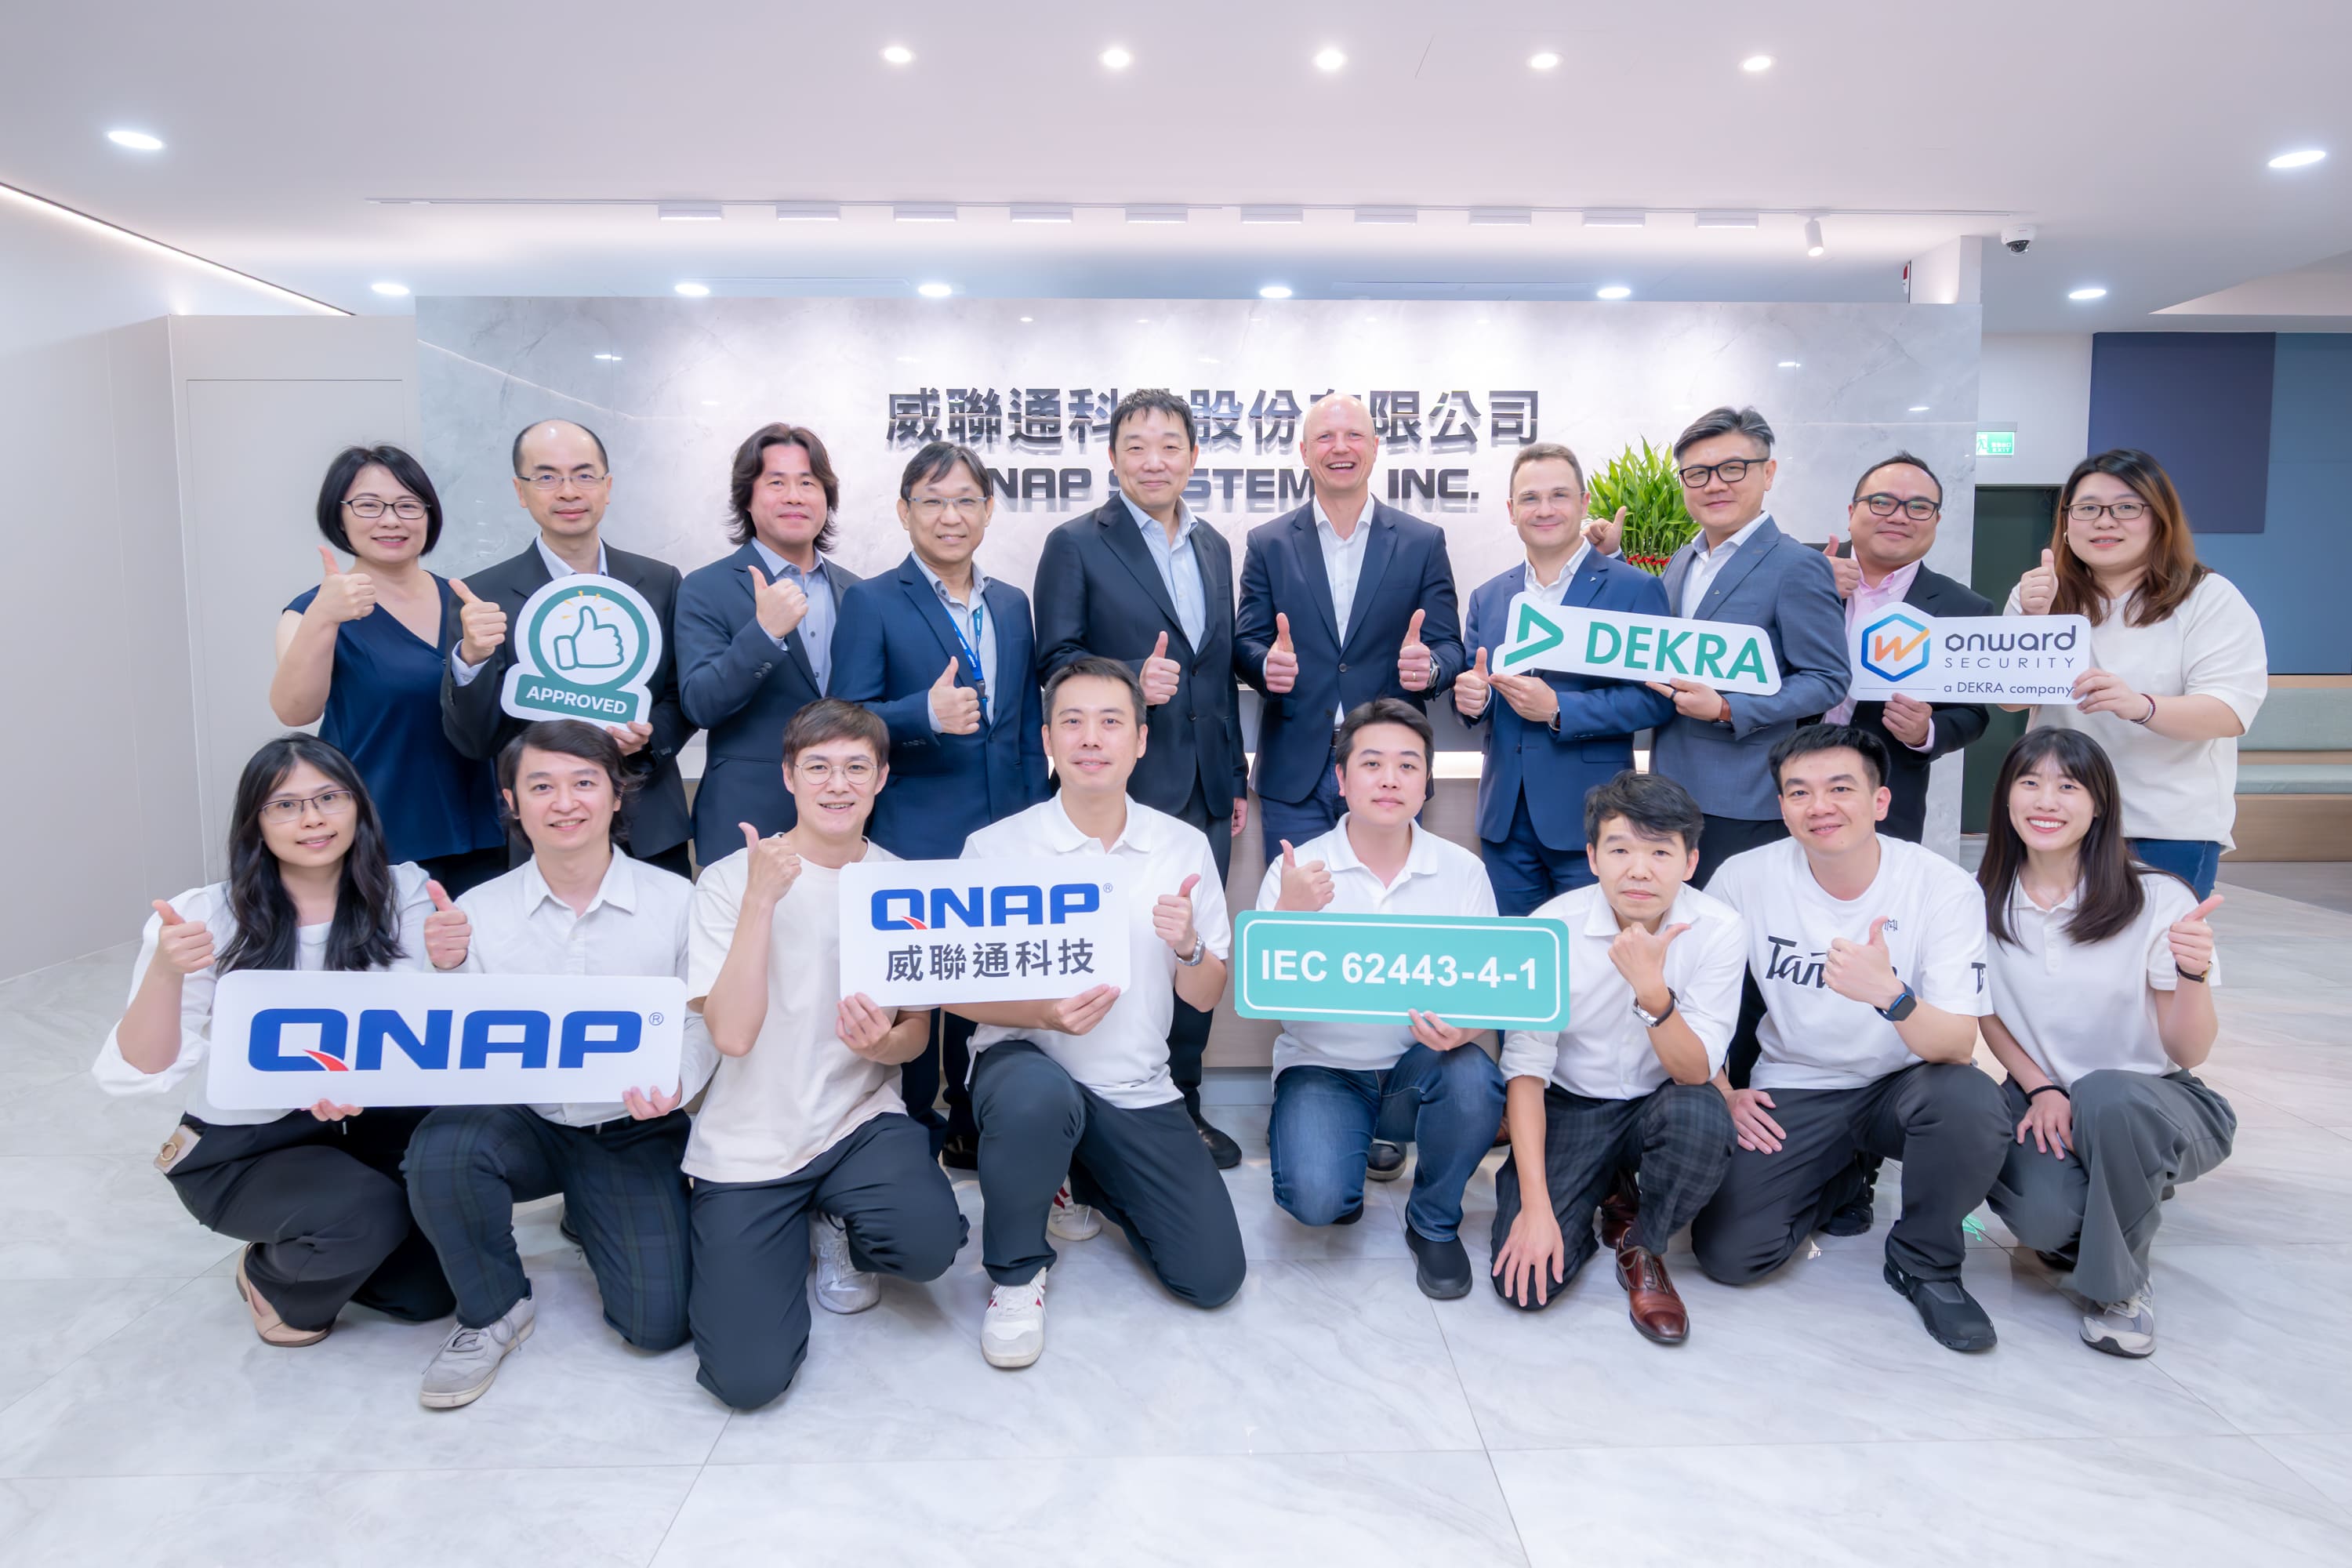
In September 2026, QNAP passed the process verification conducted by the global certification body DEKRA in accordance with the IEC 62443-4-1 standard. The core of the IEC 62443-4-1 assessment is to evaluate whether QNAP, as a supplier, can systematize and implement security requirements throughout the entire product lifecycle: from planning, design, testing, release, to ongoing maintenance. Security considerations must be built in from the very beginning (Secure by Design) of the development process.
This process validation is not limited to a single product: QNAP will continue to apply the same set of validated security development practices to every product released now and in the future, implementing secure software development (Secure SDLC).
Four verified coverage cycles: from planning to maintenance
The audit rigor of IEC 62443-4-1 is far beyond that of a one-time questionnaire review. The standard formally defines eight major secure development practices, covering Security Management, Specification of Security Requirements, Secure by Design, Secure Implementation, Security Verification and Validation Testing, Management of Security-Related Issues, Security Update Management, and Security Guidelines. It also evaluates the organization's implementation maturity according to the four-level CMMI (Capability Maturity Model Integration) model: Initial, Managed, Defined, and Improving. To pass the certification, enterprises must achieve a level of documentation, institutionalization, and cross-departmental execution that allows independent auditors to inspect each requirement in detail.
Learn about the 8 key secure development practices of the IEC 62443-4-1 standard >>
DEKRA's verification this time covers QNAP's organizational capabilities in four aspects, each of which has corresponding existing mechanisms within QNAP's current information security governance framework:
-
Secure Development Process: QNAP follows the public Secure Software Development Lifecycle (SSDLC) policy, incorporating risk assessment and threat modeling from the requirements gathering stage, and integrating them throughout architecture design and coding; the design phase must undergo security reviews covering data protection, identity authentication, access control, and encryption implementation requirements, and provides concrete secure coding standards for different programming languages; the development process introduces automated SAST (Static Application Security Testing) and DAST (Dynamic Application Security Testing) scans, complemented by penetration testing and threat model validation.
-
Information Security Risk Management: Coordinated by QNAP PSIRT (Product Security Incident Response Team), operated under a committee system, and governed by joint participation from R&D, information security, legal, customer service, and sales departments. This ensures systematic identification and assessment of information security risks throughout the product development process.
-
Security Vulnerability Management: Through a public Security Advisories notification mechanism and a Security Bounty Program, we continuously track and respond to newly discovered security vulnerabilities. For vulnerabilities reported by external researchers, QNAP PSIRT commits to completing verification and issuing a CVE number within one week.
-
Software Supply Chain Risk Management: Through the Software Supply Chain Risk Management (SSCRM) dedicated page, we publicly disclose specific practices, including maintaining SBOM (Software Bill of Materials) for QNAP NAS software and applications, using industry-standard formats such as CycloneDX and SPDX to track component composition; introducing Software Composition Analysis (SCA) and SAST automated vulnerability scanning tools into the development process, and integrating CVE data databases and CISA KEV (Known Exploited Vulnerabilities) catalog for comparison, so that third-party components and dependencies are also included in the risk management scope.
This demonstrates QNAP's organizational capability to systematize and implement security requirements throughout the entire product lifecycle, from planning to maintenance, with security governance being an established norm throughout the development process.
The supplier's own secure development capability is already within the scope of the audit.
Many compliance standards point out that when enterprises assess their own cybersecurity compliance, the security capabilities of suppliers are already part of the audit scope. For example, Article 21(2)(d) of NIS2 explicitly requires enterprises to assess the “security risks related to direct suppliers and service providers,” while Article 21(2)(e) further requires enterprises to pay attention to the secure acquisition, development, and maintenance of systems, including vulnerability management and disclosure. Possessing IEC 62443-4-1 certification is precisely the most direct third-party evidence for meeting these two requirements.
For customers who are advancing IT/OT integration and deploying in key infrastructure sectors such as smart manufacturing, energy, and transportation, this certification carries even greater significance. As NAS, edge computing unit, and IoT storage systems play an increasingly important role in these sectors, whether a supplier’s product security development process has undergone review is directly related to the overall risk exposure of the OT environment.
IEC 62443-4-1 can align with the EU Cyber Resilience Act (CRA)
The EU Cyber Resilience Act (CRA) requires that connected products ensure cybersecurity throughout their entire lifecycle. The core principles of IEC 62443-4-1 are highly consistent with those of the CRA. QNAP has obtained this certification, demonstrating that its product line is capable of meeting CRA requirements and can significantly reduce compliance risks for multinational enterprises.
Learn more: What is the EU Cyber Resilience Act (CRA)? Requirements and deadlines for NAS and Networking devices, and QNAP's approach
Comprehensive international compliance from product to operation: QNAP builds a holistic information security trust ecosystem
QNAP has obtained IEC 62443-4-1 certification, which is one of the third-party certifications accumulated in recent years. QNAP already holds multiple certifications, including ISO/IEC 27001 (Information Security Management System), ISO/IEC 27017 (Cloud Service Security Controls), ISO/IEC 27018 (Cloud Privacy Protection), and Japan's JC-STAR Level 1 (IoT Product Security Label). Now, with the addition of the IEC 62443-4-1 certification, which focuses on the "secure development process" itself, QNAP's expanding list of certifications demonstrates that its investment in information security is not just a temporary patch to meet a single regulation or customer requirement, but a long-term, systematic organizational capability building.
Visit QNAP Trust Center to view more authentication and compliance information >>
Kluczowe wnioski: Secure by Design to podstawowa koncepcja procesu rozwoju produktów QNAP
We wrześniu 2026 roku QNAP przeszedł weryfikację procesu przeprowadzoną przez globalną jednostkę certyfikującą DEKRA zgodnie ze standardem IEC 62443-4-1. Głównym celem oceny IEC 62443-4-1 jest sprawdzenie, czy QNAP jako dostawca potrafi usystematyzować i wdrożyć wymagania dotyczące bezpieczeństwa na każdym etapie cyklu życia produktu: od planowania, projektowania, testowania, wydania, aż po bieżące utrzymanie. Kwestie bezpieczeństwa muszą być uwzględnione od samego początku (Secure by Design) procesu rozwoju.
Ta walidacja procesu nie dotyczy tylko jednego produktu: QNAP będzie nadal stosować ten sam zestaw zweryfikowanych praktyk rozwoju bezpieczeństwa do każdego obecnie wydawanego i przyszłego produktu, wdrażając bezpieczny rozwój oprogramowania (Secure SDLC).
Cztery zweryfikowane cykle: od planowania do utrzymania
Rygor audytu IEC 62443-4-1 znacznie wykracza poza jednorazową ankietę. Standard formalnie definiuje osiem głównych praktyk bezpiecznego rozwoju, obejmujących Zarządzanie Bezpieczeństwem, Określenie Wymagań Bezpieczeństwa, Secure by Design, Bezpieczną Implementację, Testowanie Weryfikacji i Walidacji Bezpieczeństwa, Zarządzanie Kwestami Bezpieczeństwa, Zarządzanie Aktualizacjami Bezpieczeństwa oraz Wytyczne Bezpieczeństwa. Ocenia także dojrzałość wdrożenia organizacji według czteropoziomowego modelu CMMI (Capability Maturity Model Integration): Początkowy, Zarządzany, Zdefiniowany i Ulepszany. Aby uzyskać certyfikację, przedsiębiorstwa muszą osiągnąć poziom dokumentacji, instytucjonalizacji i realizacji międzydziałowej, który pozwala niezależnym audytorom szczegółowo sprawdzić każde wymaganie.
Poznaj 8 kluczowych praktyk bezpiecznego rozwoju według standardu IEC 62443-4-1 >>
Weryfikacja DEKRA tym razem obejmuje możliwości organizacyjne QNAP w czterech obszarach, z których każdy ma odpowiadające mu istniejące mechanizmy w obecnym systemie zarządzania bezpieczeństwem informacji QNAP:
-
Proces Bezpiecznego Rozwoju: QNAP stosuje publiczną politykę Secure Software Development Lifecycle (SSDLC), włączając ocenę ryzyka i modelowanie zagrożeń już na etapie zbierania wymagań oraz integrując je w całym projektowaniu architektury i kodowaniu; faza projektowania musi przejść przeglądy bezpieczeństwa obejmujące ochronę danych, uwierzytelnianie tożsamości, kontrolę dostępu i wymagania dotyczące wdrożenia szyfrowania, a także zapewnia konkretne standardy bezpiecznego kodowania dla różnych języków programowania; w procesie rozwoju wprowadzane są automatyczne skanowania SAST (Statyczne Testy Bezpieczeństwa Aplikacji) i DAST (Dynamiczne Testy Bezpieczeństwa Aplikacji), uzupełnione testami penetracyjnymi i walidacją modelu zagrożeń.
-
Zarządzanie Ryzykiem Bezpieczeństwa Informacji: Koordynowane przez QNAP PSIRT (Product Security Incident Response Team), działające w systemie komitetowym i zarządzane przy wspólnym udziale działów R&D, bezpieczeństwa informacji, prawnego, obsługi klienta i sprzedaży. Zapewnia to systematyczną identyfikację i ocenę ryzyk bezpieczeństwa informacji na każdym etapie rozwoju produktu.
-
Zarządzanie Lukami Bezpieczeństwa: Poprzez publiczny mechanizm powiadamiania Security Advisories oraz program Security Bounty, nieustannie śledzimy i reagujemy na nowo wykryte luki bezpieczeństwa. W przypadku luk zgłaszanych przez zewnętrznych badaczy, QNAP PSIRT zobowiązuje się do zakończenia weryfikacji i nadania numeru CVE w ciągu tygodnia.
-
Zarządzanie Ryzykiem Łańcucha Dostaw Oprogramowania: Poprzez dedykowaną stronę Software Supply Chain Risk Management (SSCRM) publicznie ujawniamy konkretne praktyki, w tym utrzymywanie SBOM (Software Bill of Materials) dla oprogramowania i aplikacji QNAP NAS, korzystanie z branżowych formatów takich jak CycloneDX i SPDX do śledzenia składu komponentów; wprowadzamy narzędzia do analizy składu oprogramowania (SCA) i automatycznego skanowania podatności SAST do procesu rozwoju oraz integrujemy bazy danych CVE i katalog CISA KEV (Known Exploited Vulnerabilities) do porównań, aby komponenty i zależności stron trzecich również były objęte zakresem zarządzania ryzykiem.
To pokazuje zdolność organizacyjną QNAP do systematyzowania i wdrażania wymagań bezpieczeństwa na każdym etapie cyklu życia produktu, od planowania po utrzymanie, gdzie zarządzanie bezpieczeństwem jest stałą normą w całym procesie rozwoju.
Własna zdolność dostawcy do bezpiecznego rozwoju jest już objęta zakresem audytu.
Wiele standardów zgodności wskazuje, że podczas oceny własnej zgodności cyberbezpieczeństwa przez przedsiębiorstwa, możliwości bezpieczeństwa dostawców są już częścią zakresu audytu. Na przykład artykuł 21(2)(d) NIS2 wyraźnie wymaga od przedsiębiorstw oceny „ryzyk bezpieczeństwa związanych z bezpośrednimi dostawcami i usługodawcami”, a artykuł 21(2)(e) dodatkowo nakazuje zwrócenie uwagi na bezpieczne pozyskiwanie, rozwój i utrzymanie systemów, w tym zarządzanie i ujawnianie podatności. Posiadanie certyfikatu IEC 62443-4-1 jest właśnie najbardziej bezpośrednim dowodem zewnętrznym na spełnienie tych dwóch wymagań.
Dla klientów wdrażających integrację IT/OT i działających w kluczowych sektorach infrastruktury, takich jak inteligentna produkcja, energetyka czy transport, certyfikat ten ma jeszcze większe znaczenie. Ponieważ systemy NAS, jednostki edge computing i magazyny IoT odgrywają coraz ważniejszą rolę w tych sektorach, to czy proces rozwoju bezpieczeństwa produktu dostawcy został poddany przeglądowi, ma bezpośredni wpływ na ogólną ekspozycję ryzyka środowiska OT.
IEC 62443-4-1 może być zgodny z unijnym Cyber Resilience Act (CRA)
Unijny Cyber Resilience Act (CRA) wymaga, aby produkty połączone zapewniały cyberbezpieczeństwo przez cały cykl życia. Główne zasady IEC 62443-4-1 są wysoce spójne z zasadami CRA. QNAP uzyskał ten certyfikat, co pokazuje, że jego linia produktów jest w stanie spełnić wymagania CRA i znacząco ograniczyć ryzyka zgodności dla międzynarodowych przedsiębiorstw.
Dowiedz się więcej: Czym jest unijny Cyber Resilience Act (CRA)? Wymagania i terminy dla urządzeń NAS i sieciowych oraz podejście QNAP
Kompleksowa zgodność międzynarodowa od produktu po operacje: QNAP buduje holistyczny ekosystem zaufania w zakresie bezpieczeństwa informacji
QNAP uzyskał certyfikat IEC 62443-4-1, który jest jednym z certyfikatów zewnętrznych zdobytych w ostatnich latach. QNAP posiada już wiele certyfikatów, w tym ISO/IEC 27001 (System Zarządzania Bezpieczeństwem Informacji), ISO/IEC 27017 (Kontrole Bezpieczeństwa Usług Chmurowych), ISO/IEC 27018 (Ochrona Prywatności w Chmurze) oraz japoński JC-STAR Poziom 1 (Etykieta Bezpieczeństwa Produktów IoT). Teraz, wraz z uzyskaniem certyfikatu IEC 62443-4-1, który koncentruje się na samym „procesie bezpiecznego rozwoju”, rosnąca lista certyfikatów QNAP pokazuje, że inwestycja w bezpieczeństwo informacji nie jest tylko tymczasową łatką na potrzeby pojedynczego przepisu czy klienta, lecz długoterminowym, systematycznym budowaniem zdolności organizacyjnych.
Odwiedź QNAP Trust Center, aby zobaczyć więcej informacji o uwierzytelnieniach i zgodności >>


 5 min czytania