Key takeaway: Secure by Design is the core concept of QNAP's product development process
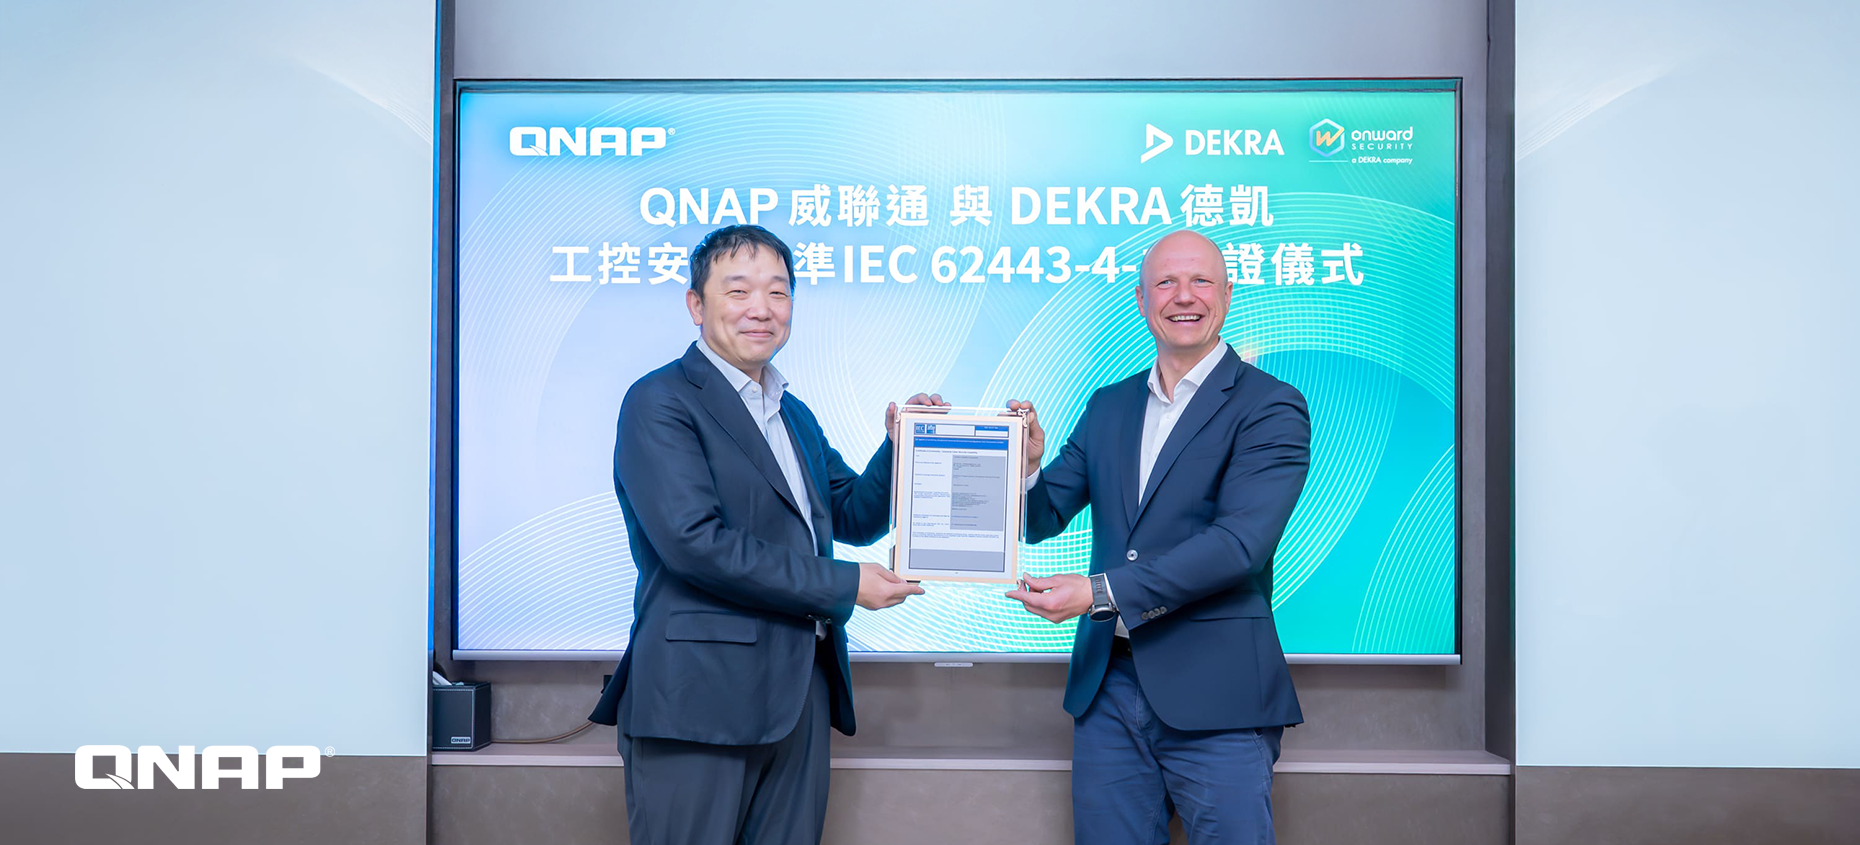
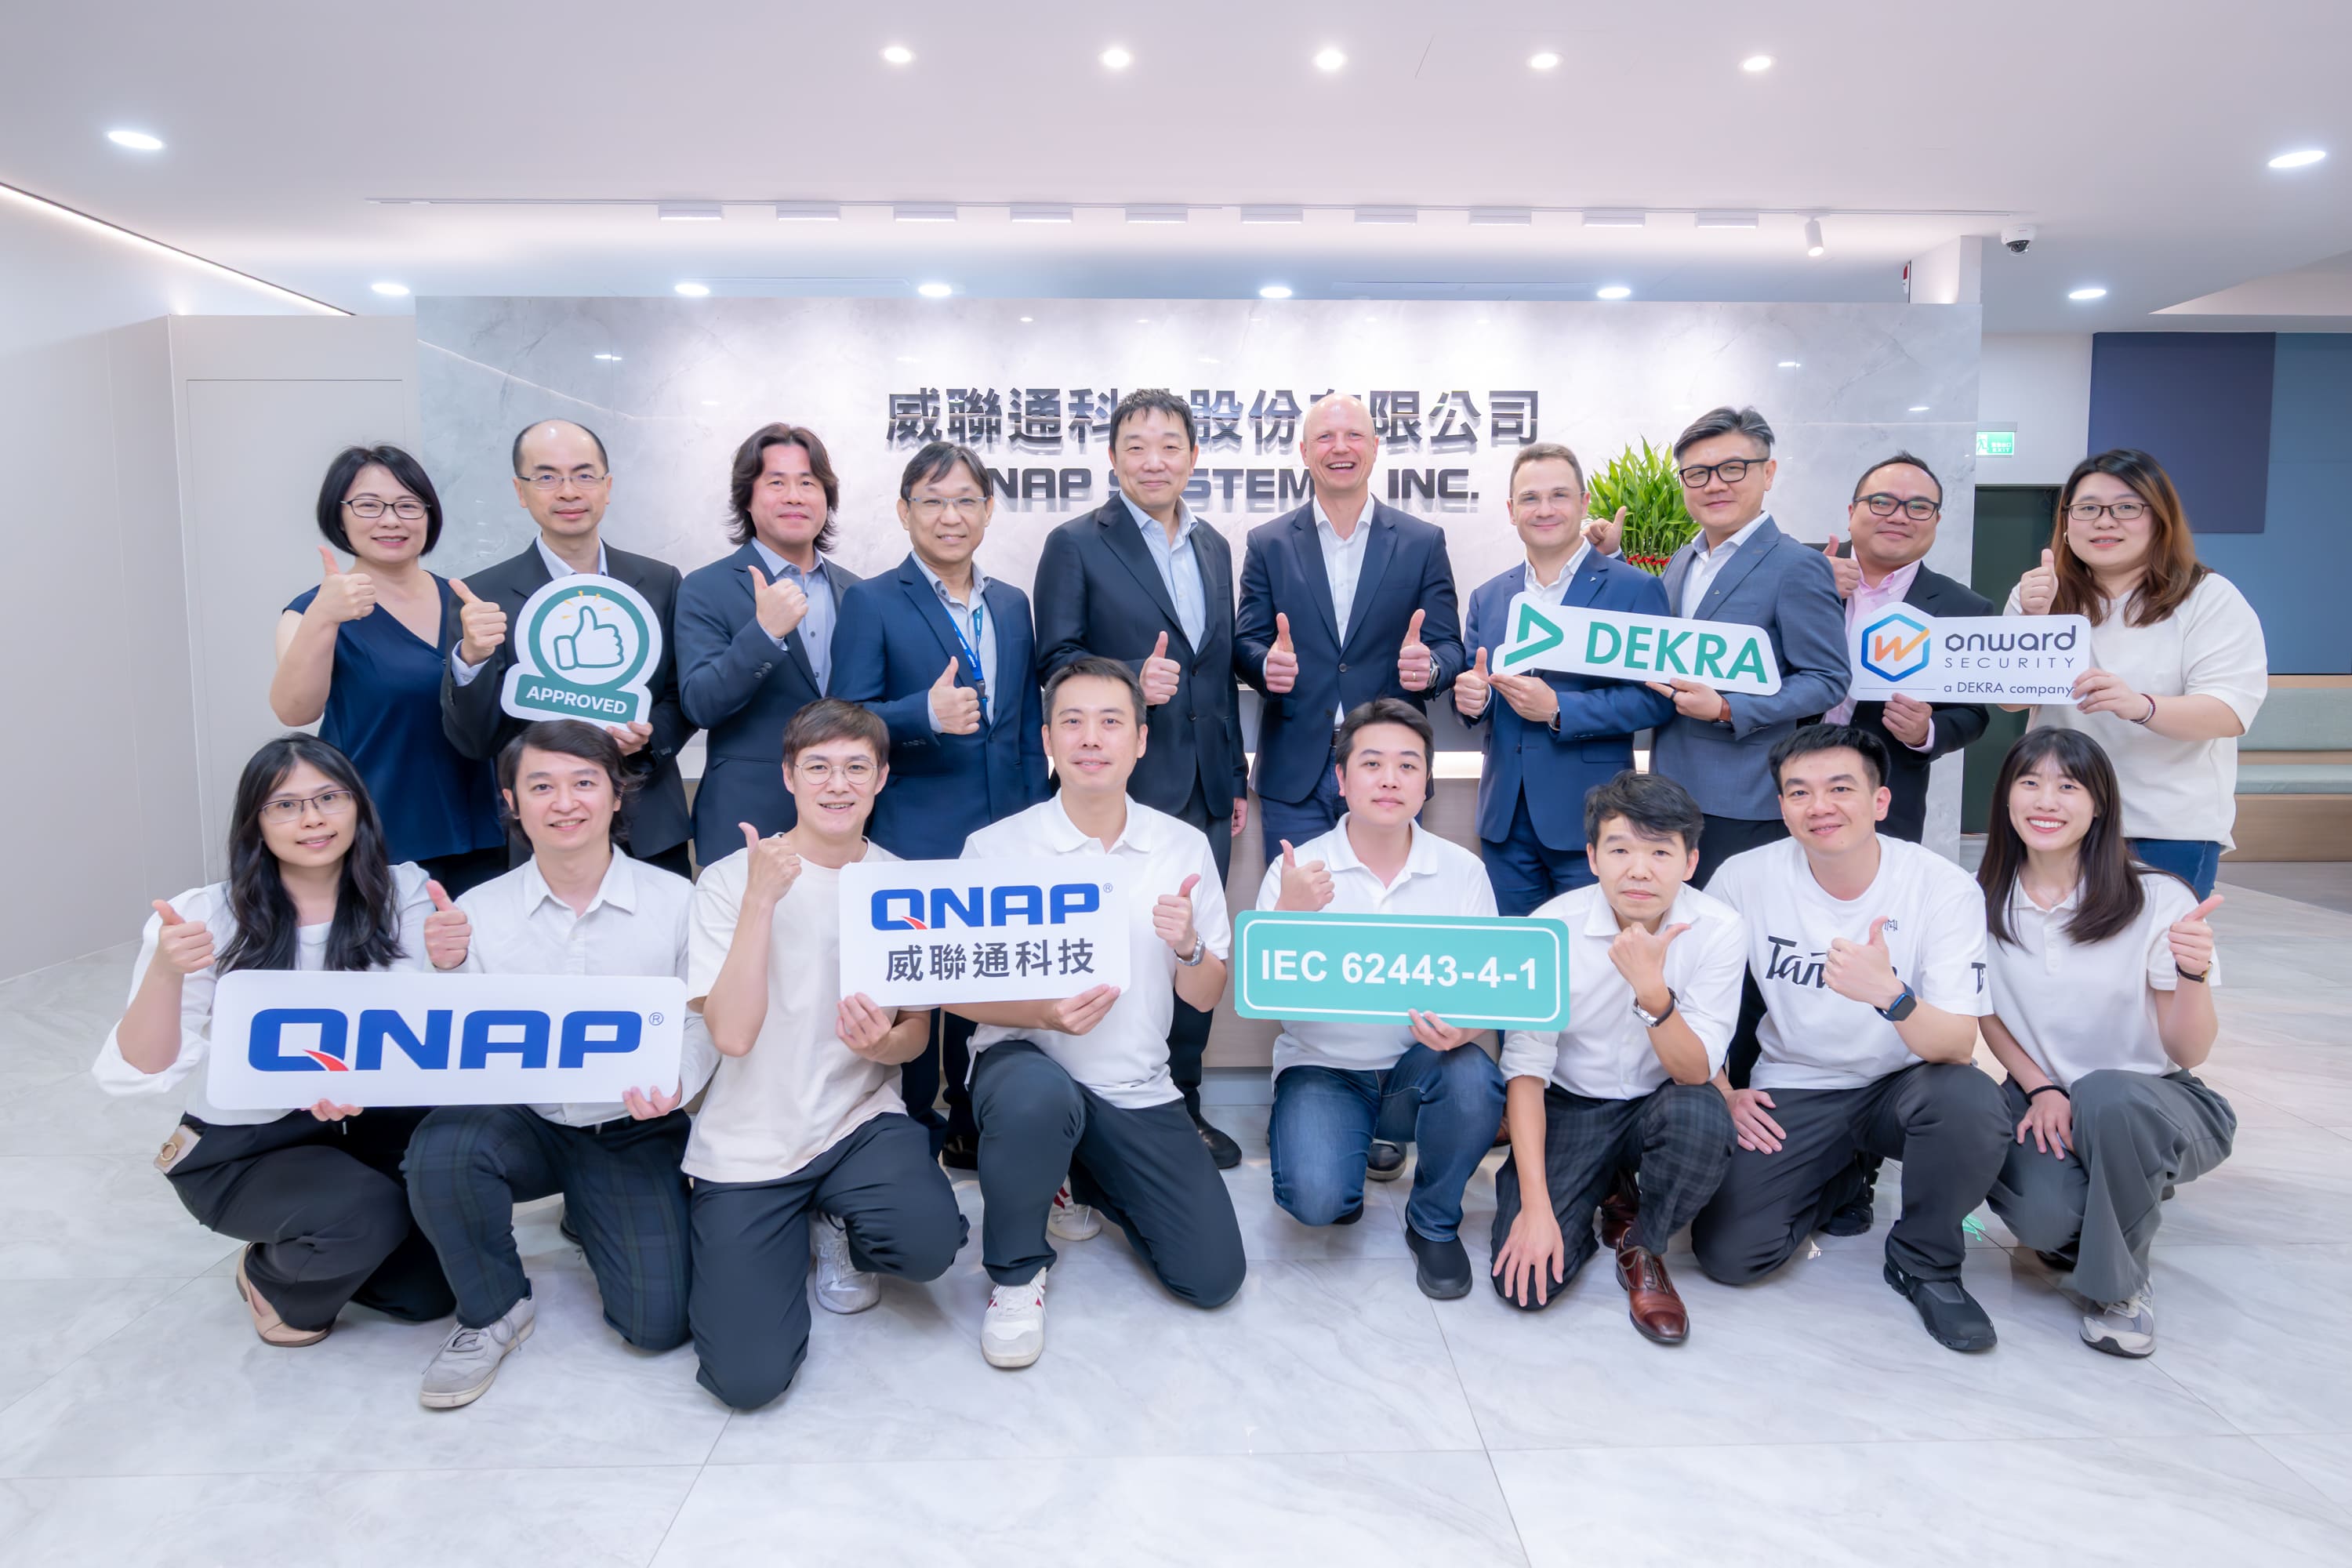
In September 2026, QNAP passed the process verification conducted by the global certification body DEKRA in accordance with the IEC 62443-4-1 standard. The core of the IEC 62443-4-1 assessment is to evaluate whether QNAP, as a supplier, can systematize and implement security requirements throughout the entire product lifecycle: from planning, design, testing, release, to ongoing maintenance. Security considerations must be built in from the very beginning (Secure by Design) of the development process.
This process validation is not limited to a single product: QNAP will continue to apply the same set of validated security development practices to every product released now and in the future, implementing secure software development (Secure SDLC).
Four verified coverage cycles: from planning to maintenance
The audit rigor of IEC 62443-4-1 is far beyond that of a one-time questionnaire review. The standard formally defines eight major secure development practices, covering Security Management, Specification of Security Requirements, Secure by Design, Secure Implementation, Security Verification and Validation Testing, Management of Security-Related Issues, Security Update Management, and Security Guidelines. It also evaluates the organization's implementation maturity according to the four-level CMMI (Capability Maturity Model Integration) model: Initial, Managed, Defined, and Improving. To pass the certification, enterprises must achieve a level of documentation, institutionalization, and cross-departmental execution that allows independent auditors to inspect each requirement in detail.
Learn about the 8 key secure development practices of the IEC 62443-4-1 standard >>
DEKRA's verification this time covers QNAP's organizational capabilities in four aspects, each of which has corresponding existing mechanisms within QNAP's current information security governance framework:
-
Secure Development Process: QNAP follows the public Secure Software Development Lifecycle (SSDLC) policy, incorporating risk assessment and threat modeling from the requirements gathering stage, and integrating them throughout architecture design and coding; the design phase must undergo security reviews covering data protection, identity authentication, access control, and encryption implementation requirements, and provides concrete secure coding standards for different programming languages; the development process introduces automated SAST (Static Application Security Testing) and DAST (Dynamic Application Security Testing) scans, complemented by penetration testing and threat model validation.
-
Information Security Risk Management: Coordinated by QNAP PSIRT (Product Security Incident Response Team), operated under a committee system, and governed by joint participation from R&D, information security, legal, customer service, and sales departments. This ensures systematic identification and assessment of information security risks throughout the product development process.
-
Security Vulnerability Management: Through a public Security Advisories notification mechanism and a Security Bounty Program, we continuously track and respond to newly discovered security vulnerabilities. For vulnerabilities reported by external researchers, QNAP PSIRT commits to completing verification and issuing a CVE number within one week.
-
Software Supply Chain Risk Management: Through the Software Supply Chain Risk Management (SSCRM) dedicated page, we publicly disclose specific practices, including maintaining SBOM (Software Bill of Materials) for QNAP NAS software and applications, using industry-standard formats such as CycloneDX and SPDX to track component composition; introducing Software Composition Analysis (SCA) and SAST automated vulnerability scanning tools into the development process, and integrating CVE data databases and CISA KEV (Known Exploited Vulnerabilities) catalog for comparison, so that third-party components and dependencies are also included in the risk management scope.
This demonstrates QNAP's organizational capability to systematize and implement security requirements throughout the entire product lifecycle, from planning to maintenance, with security governance being an established norm throughout the development process.
The supplier's own secure development capability is already within the scope of the audit.
Many compliance standards point out that when enterprises assess their own cybersecurity compliance, the security capabilities of suppliers are already part of the audit scope. For example, Article 21(2)(d) of NIS2 explicitly requires enterprises to assess the “security risks related to direct suppliers and service providers,” while Article 21(2)(e) further requires enterprises to pay attention to the secure acquisition, development, and maintenance of systems, including vulnerability management and disclosure. Possessing IEC 62443-4-1 certification is precisely the most direct third-party evidence for meeting these two requirements.
For customers who are advancing IT/OT integration and deploying in key infrastructure sectors such as smart manufacturing, energy, and transportation, this certification carries even greater significance. As NAS, edge computing unit, and IoT storage systems play an increasingly important role in these sectors, whether a supplier’s product security development process has undergone review is directly related to the overall risk exposure of the OT environment.
IEC 62443-4-1 can align with the EU Cyber Resilience Act (CRA)
The EU Cyber Resilience Act (CRA) requires that connected products ensure cybersecurity throughout their entire lifecycle. The core principles of IEC 62443-4-1 are highly consistent with those of the CRA. QNAP has obtained this certification, demonstrating that its product line is capable of meeting CRA requirements and can significantly reduce compliance risks for multinational enterprises.
Learn more: What is the EU Cyber Resilience Act (CRA)? Requirements and deadlines for NAS and Networking devices, and QNAP's approach
Comprehensive international compliance from product to operation: QNAP builds a holistic information security trust ecosystem
QNAP has obtained IEC 62443-4-1 certification, which is one of the third-party certifications accumulated in recent years. QNAP already holds multiple certifications, including ISO/IEC 27001 (Information Security Management System), ISO/IEC 27017 (Cloud Service Security Controls), ISO/IEC 27018 (Cloud Privacy Protection), and Japan's JC-STAR Level 1 (IoT Product Security Label). Now, with the addition of the IEC 62443-4-1 certification, which focuses on the "secure development process" itself, QNAP's expanding list of certifications demonstrates that its investment in information security is not just a temporary patch to meet a single regulation or customer requirement, but a long-term, systematic organizational capability building.
Visit QNAP Trust Center to view more authentication and compliance information >>
Temel çıkarım: Secure by Design, QNAP'ın ürün geliştirme sürecinin temel konseptidir
Eylül 2026'da QNAP, küresel sertifikasyon kuruluşu DEKRA tarafından IEC 62443-4-1 standardına uygun olarak gerçekleştirilen süreç doğrulamasını başarıyla geçti. IEC 62443-4-1 değerlendirmesinin özü, QNAP'ın bir tedarikçi olarak güvenlik gereksinimlerini ürün yaşam döngüsünün tamamında (planlama, tasarım, test, yayınlama ve sürekli bakım) sistematikleştirip uygulayabilme yeteneğini değerlendirmektir. Güvenlik önlemleri, geliştirme sürecinin en başından itibaren (Secure by Design) dahil edilmelidir.
Bu süreç doğrulaması tek bir ürünle sınırlı değildir: QNAP, doğrulanmış güvenli yazılım geliştirme uygulamalarını şimdi ve gelecekte piyasaya sürülecek her ürüne uygulamaya devam edecek, güvenli yazılım geliştirme (Secure SDLC) uygulayacaktır.
Dört doğrulanmış kapsama döngüsü: planlamadan bakıma
IEC 62443-4-1'in denetim titizliği, tek seferlik bir anket incelemesinin çok ötesindedir. Standart, Güvenlik Yönetimi, Güvenlik Gereksinimlerinin Belirlenmesi, Secure by Design, Güvenli Uygulama, Güvenlik Doğrulama ve Geçerlilik Testi, Güvenlikle İlgili Sorunların Yönetimi, Güvenlik Güncelleme Yönetimi ve Güvenlik Kılavuzları dahil olmak üzere sekiz ana güvenli geliştirme uygulamasını resmi olarak tanımlar. Ayrıca, kuruluşun uygulama olgunluğunu dört seviyeli CMMI (Yetenek Olgunluk Modeli Entegrasyonu) modeliyle değerlendirir: Başlangıç, Yönetilen, Tanımlı ve İyileştirilen. Sertifikayı geçmek için işletmelerin, bağımsız denetçilerin her gereksinimi ayrıntılı olarak inceleyebileceği bir dokümantasyon, kurumsallaşma ve departmanlar arası yürütme seviyesine ulaşması gerekir.
IEC 62443-4-1 standardının 8 temel güvenli geliştirme uygulamasını öğrenin >>
Bu kez DEKRA'nın doğrulaması, QNAP'ın mevcut bilgi güvenliği yönetim çerçevesi içinde her biri karşılık gelen mevcut mekanizmalara sahip olan dört alandaki organizasyonel yeteneklerini kapsamaktadır:
-
Güvenli Geliştirme Süreci: QNAP, gereksinim toplama aşamasından itibaren risk değerlendirmesi ve tehdit modellemesini içeren, mimari tasarım ve kodlama boyunca entegre eden kamuya açık Güvenli Yazılım Geliştirme Yaşam Döngüsü (SSDLC) politikasını izler; tasarım aşaması, veri koruma, kimlik doğrulama, erişim kontrolü ve şifreleme uygulama gereksinimlerini kapsayan güvenlik incelemelerinden geçmeli ve farklı programlama dilleri için somut güvenli kodlama standartları sağlamalıdır; geliştirme sürecine otomatik SAST (Statik Uygulama Güvenlik Testi) ve DAST (Dinamik Uygulama Güvenlik Testi) taramaları dahil edilir, ayrıca penetrasyon testi ve tehdit modeli doğrulaması ile desteklenir.
-
Bilgi Güvenliği Risk Yönetimi: QNAP PSIRT (Ürün Güvenliği Olay Müdahale Ekibi) tarafından koordine edilir, komite sistemiyle çalışır ve Ar-Ge, bilgi güvenliği, hukuk, müşteri hizmetleri ve satış departmanlarının ortak katılımıyla yönetilir. Bu, ürün geliştirme süreci boyunca bilgi güvenliği risklerinin sistematik olarak tanımlanmasını ve değerlendirilmesini sağlar.
-
Güvenlik Açığı Yönetimi: Kamuya açık Güvenlik Duyuruları bildirim mekanizması ve Güvenlik Ödül Programı aracılığıyla yeni keşfedilen güvenlik açıklarını sürekli olarak takip eder ve yanıtlarız. Dış araştırmacılar tarafından bildirilen açıklar için QNAP PSIRT, doğrulamayı tamamlamayı ve bir CVE numarası yayınlamayı bir hafta içinde taahhüt eder.
-
Yazılım Tedarik Zinciri Risk Yönetimi: Yazılım Tedarik Zinciri Risk Yönetimi (SSCRM) özel sayfası aracılığıyla, QNAP NAS yazılımı ve uygulamaları için SBOM (Yazılım Malzeme Listesi) tutmak, bileşen bileşimini izlemek için CycloneDX ve SPDX gibi sektör standartı formatları kullanmak dahil olmak üzere belirli uygulamaları kamuya açık şekilde açıklıyoruz; geliştirme sürecine Yazılım Bileşimi Analizi (SCA) ve SAST otomatik güvenlik açığı tarama araçlarını dahil ediyor, CVE veri tabanları ve CISA KEV (Bilinen Sömürülen Açıklar) kataloğunu karşılaştırma için entegre ediyoruz, böylece üçüncü taraf bileşenler ve bağımlılıklar da risk yönetimi kapsamına dahil ediliyor.
Bu, QNAP'ın güvenlik gereksinimlerini ürün yaşam döngüsünün tamamında, planlamadan bakıma kadar sistematikleştirip uygulayabilme organizasyonel yeteneğini ve güvenlik yönetiminin geliştirme sürecinin her aşamasında yerleşik bir norm olduğunu göstermektedir.
Tedarikçinin kendi güvenli geliştirme yeteneği zaten denetim kapsamındadır.
Birçok uyumluluk standardı, işletmeler kendi siber güvenlik uyumluluklarını değerlendirirken tedarikçilerin güvenlik yeteneklerinin de denetim kapsamına dahil olduğunu belirtir. Örneğin, NIS2'nin 21(2)(d) maddesi, işletmelerin “doğrudan tedarikçiler ve hizmet sağlayıcılarla ilgili güvenlik risklerini” değerlendirmesini açıkça gerektirirken, 21(2)(e) maddesi ise sistemlerin güvenli edinimi, geliştirilmesi ve bakımı, açık yönetimi ve ifşası konularına dikkat edilmesini ister. IEC 62443-4-1 sertifikasına sahip olmak, bu iki gereksinimi karşılamak için en doğrudan üçüncü taraf kanıtıdır.
BT/OT entegrasyonunu ilerleten ve akıllı üretim, enerji ve ulaşım gibi kritik altyapı sektörlerinde dağıtım yapan müşteriler için bu sertifika çok daha büyük bir anlam taşır. NAS, edge computing birimi ve IoT depolama sistemleri bu sektörlerde giderek daha önemli bir rol oynadıkça, bir tedarikçinin ürün güvenliği geliştirme sürecinin denetimden geçip geçmediği, OT ortamının genel risk maruziyetiyle doğrudan ilişkilidir.
IEC 62443-4-1, AB Siber Dayanıklılık Yasası (CRA) ile uyumlu olabilir
AB Siber Dayanıklılık Yasası (CRA), bağlı ürünlerin tüm yaşam döngüleri boyunca siber güvenliği sağlamasını gerektirir. IEC 62443-4-1'in temel ilkeleri, CRA'nın ilkeleriyle yüksek oranda örtüşmektedir. QNAP bu sertifikayı alarak ürün serisinin CRA gereksinimlerini karşılayabildiğini ve çok uluslu şirketler için uyumluluk risklerini önemli ölçüde azaltabileceğini göstermektedir.
Daha fazla bilgi edinin: AB Siber Dayanıklılık Yasası (CRA) nedir? NAS ve Ağ cihazları için gereksinimler ve son tarihler ile QNAP'ın yaklaşımı
Üründen operasyona kapsamlı uluslararası uyumluluk: QNAP bütünsel bir bilgi güvenliği güven ekosistemi inşa ediyor
QNAP, son yıllarda elde edilen üçüncü taraf sertifikalardan biri olan IEC 62443-4-1 sertifikasını aldı. QNAP, halihazırda ISO/IEC 27001 (Bilgi Güvenliği Yönetim Sistemi), ISO/IEC 27017 (Bulut Hizmeti Güvenlik Kontrolleri), ISO/IEC 27018 (Bulut Gizlilik Koruması) ve Japonya'nın JC-STAR Seviye 1 (IoT Ürün Güvenlik Etiketi) dahil olmak üzere birçok sertifikaya sahiptir. Şimdi ise, doğrudan "güvenli geliştirme süreci"ne odaklanan IEC 62443-4-1 sertifikasının eklenmesiyle, QNAP'ın artan sertifika listesi, bilgi güvenliğine yapılan yatırımın yalnızca tek bir düzenleme veya müşteri gereksinimini karşılamak için geçici bir yama değil, uzun vadeli ve sistematik bir organizasyonel yetenek inşası olduğunu göstermektedir.
Daha fazla kimlik doğrulama ve uyumluluk bilgisi için QNAP Trust Center'ı ziyaret edin >>


 5 dk okuma