Key Takeaway: QNAP has completed the first phase of EU CRA compliance
QNAP completed the first phase of its EU Cyber Resilience Act (CRA) compliance program on September 11, 2026 — the same day the CRA's obligation to report actively exploited vulnerabilities and severe incidents took effect.
-
Incident reporting: The QNAP Security Reporting Platform is now live. QNAP initiates its statutory response process within 24 hours of receiving a report.
-
Secure development: QNAP follows a publicly available Secure Software Development Lifecycle (SSDLC) policy and has passed IEC 62443-4-1 process verification.
-
Vulnerability management: QNAP PSIRT coordinates vulnerability handling and commits to verifying externally reported vulnerabilities and assigning CVE IDs within one week.
-
Supply chain transparency: QNAP maintains SBOMs in CycloneDX and SPDX formats and cross-checks them against CVE databases and the CISA Known Exploited Vulnerabilities (KEV) catalog.
-
Coverage: QNAP's entire product portfolio, including enterprise ZFS storage, business NAS, Edge AI NAS, and all networking products (routers and switches).
What is the EU Cyber Resilience Act (CRA)?
The EU Cyber Resilience Act (CRA), Regulation (EU) 2024/2847, requires every product with digital elements (PwDE) sold in the EU to meet mandatory cybersecurity requirements throughout its entire lifecycle. CRA compliance is a prerequisite for the CE marking, and products without a CE marking cannot be placed on the EU market.
Three Goals of the CRA
- Strengthen the overall resilience of the EU digital market.
- Give users clearer visibility into the security of the products they buy.
- Reduce the number of vulnerabilities in digital products after they reach the market.
Which Products Does the CRA Cover?
The CRA covers any hardware or software that can connect, directly or indirectly, to a device or network — including its remote data processing solutions. NAS devices, routers, switches, operating systems, and applications all fall within scope. Medical devices, motor vehicles, civil aviation, and marine equipment are excluded because they are already governed by equivalent regulations.
Core Obligations for All Manufacturers Under the CRA
- Conduct a cybersecurity risk assessment at the design stage, applying Secure by Design and Secure by Default principles.
- Establish a vulnerability handling process that meets CRA requirements.
- Provide security updates throughout the support period, until the product reaches end of support.
- Prepare technical documentation, complete a conformity assessment, and affix the CE marking (applies from December 11, 2027).
- Provide clear instructions for secure use, the end-of-support date, and a point of contact for vulnerability reporting.
- Report actively exploited vulnerabilities and severe incidents to the relevant authorities.
When does the CRA take effect? Three key dates
The CRA is being phased in: reporting of actively exploited vulnerabilities became mandatory on September 11, 2026, and full compliance is required for all products placed on the EU market from December 11, 2027.
| Date |
Milestone |
QNAP status |
| December 10, 2024 |
CRA enters into force; transition period begins |
CRA compliance program launched |
| September 11, 2026 |
Reporting obligations for actively exploited vulnerabilities and severe incidents apply |
First phase completed; Security Reporting Platform live |
| December 11, 2027 |
Full compliance deadline, including pre-market conformity assessment and CE marking |
Ongoing, in line with EU guidance and harmonised standards |
Source: European Commission – Cyber Resilience Act
How is the CRA different from NIS2, and why look at them together?
The CRA regulates products; NIS2 regulates organizations. Where they overlap is a unified, risk-based strategy that secures the digital supply chain. For an organization to comply with NIS2, the equipment it buys must itself comply with the CRA.
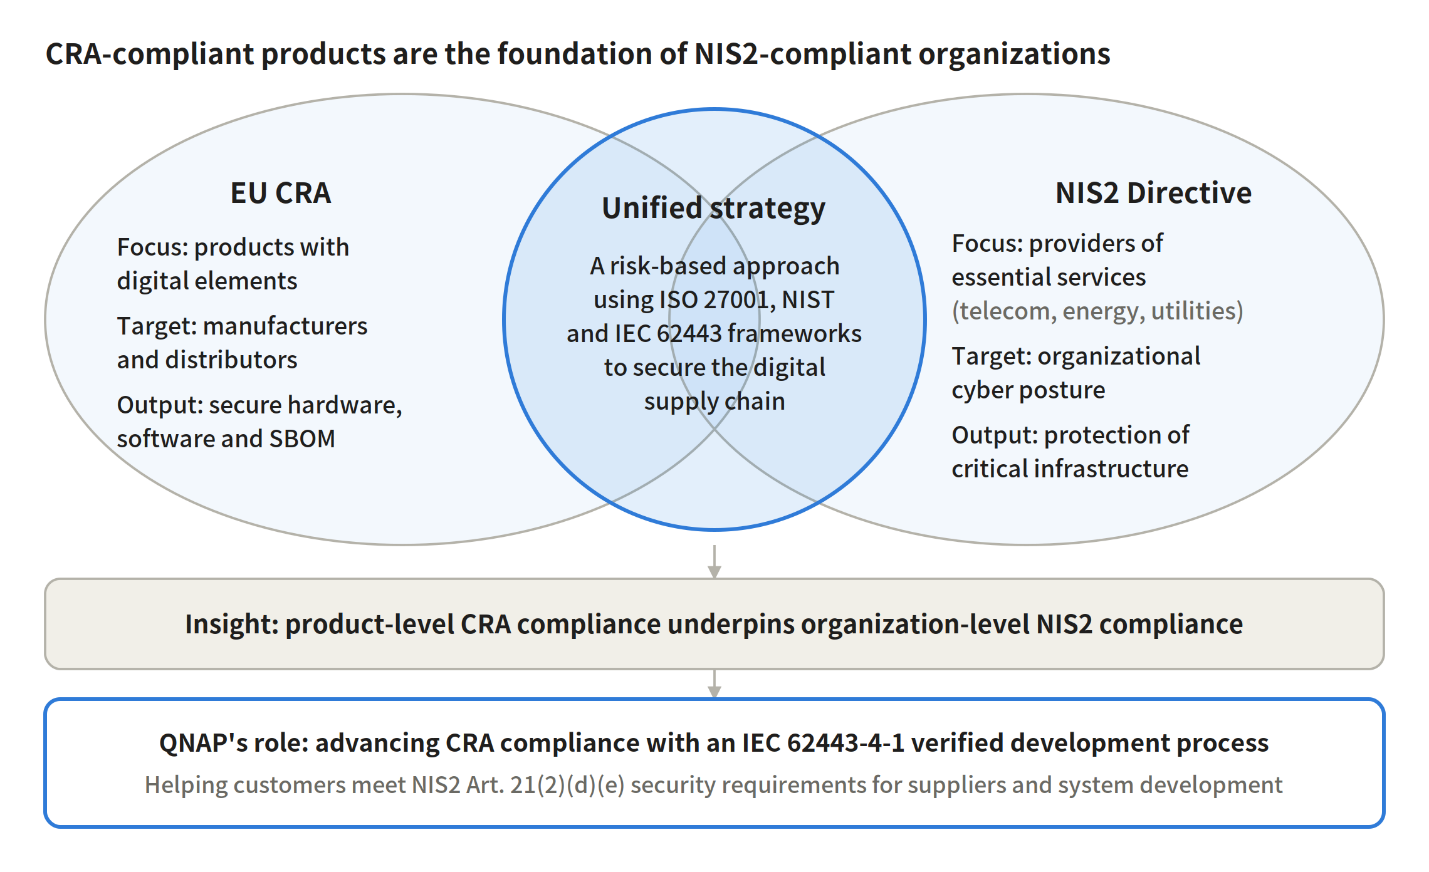
How the CRA and NIS2 relate a unified strategy from products to organizations
|
EU CRA |
EU NIS2 Directive |
| Focus |
Cybersecurity of products with digital elements |
Security of network and information systems at essential and important entities |
| Who it applies to |
Manufacturers, importers, and distributors |
Organizations in energy, transport, telecom, healthcare, utilities, and other sectors |
| Expected outcome |
Secure hardware and software with transparent components |
Organizational cybersecurity governance and critical infrastructure protection |
| Relevance to QNAP |
QNAP must comply directly as a manufacturer |
QNAP customers must assess supplier security; QNAP provides verifiable evidence |
NIS2 Article 21(2)(d) requires organizations to assess the security risks of their direct suppliers and service providers. Article 21(2)(e) requires security in the acquisition, development, and maintenance of systems, including vulnerability handling and disclosure. QNAP's IEC 62443-4-1 verification, public vulnerability disclosure process, and completion of the first phase of CRA compliance can serve as third-party evidence when customers assess their suppliers.
Learn more: Choose QNAP solutions to achieve EU NIS2 network security and supply chain risk management
How does QNAP meet CRA requirements? Four pillars
QNAP addresses the CRA's essential cybersecurity requirements through four pillars: a secure development process verified against international standards, 24-hour incident reporting, proactive vulnerability management, and a transparent software supply chain. These mechanisms were in place before the CRA took effect — they are not a last-minute fix for a single regulation.
Pillar 1: A secure development lifecycle verified against IEC 62443-4-1
IEC 62443-4-1 is the International Electrotechnical Commission (IEC) standard for secure product development lifecycles. It defines eight secure development practices and assesses how well an organization implements them across four maturity levels. QNAP passed DEKRA's IEC 62443-4-1 process verification in September 2026. Because the verification covers the entire development process, it applies to every product QNAP releases now and in the future.
- Risk assessment and threat modeling begin at the requirements stage.
- Designs must pass a security review covering data protection, authentication, access control, and encryption.
- Development includes automated static (SAST) and dynamic (DAST) application security testing, complemented by penetration testing.
Pillar 2: CRA-aligned 24-hour incident reporting
The QNAP Security Reporting Platform serves as QNAP's single point of contact for CRA reporting. Customers, end users, and security researchers worldwide can use it to report actively exploited vulnerabilities or severe security incidents. Within 24 hours of receiving a report, QNAP initiates its statutory response process, assesses the risk, and releases security updates.
Pillar 3: PSIRT-led vulnerability management
The QNAP Product Security Incident Response Team (PSIRT) operates as a committee, with members from R&D, information security, legal, and customer service. QNAP tracks new vulnerabilities through its public Security Advisories and Security Bounty Program. For vulnerabilities reported by external researchers, PSIRT commits to completing verification and assigning a CVE ID within one week.
Pillar 4: A transparent software supply chain with SBOMs
The CRA requires manufacturers to create a Software Bill of Materials (SBOM) and provide it to authorities on request. QNAP maintains SBOMs for its NAS software and applications in the industry-standard CycloneDX and SPDX formats. Its development process includes Software Composition Analysis (SCA) and cross-checks components against CVE databases and the U.S. CISA Known Exploited Vulnerabilities (KEV) catalog, bringing third-party and open-source components under risk management.
User transparency: Clearly stated support periods
The CRA requires manufacturers to disclose each product's intended use, end-of-support date, and vulnerability reporting contact. Users can check each model's support period on the QNAP Product Support Status page and harden their settings with the NAS Security Guide.
Which QNAP products are covered by CRA compliance?
QNAP's CRA security and reporting mechanisms cover its entire product portfolio and are backed by multiple independent international certifications.
| Product category |
Representative product lines |
| Enterprise storage |
ZFS storage, dual-controller NAS, all-flash NAS |
| Business and multimedia NAS |
QTS / QuTS hero business NAS, NAS for creators and home users |
| AI computing |
Edge AI NAS solutions |
| Networking |
Routers, switches |
QNAP's investment in cybersecurity is a long-term, systematic organizational capability that spans product development, cloud services, and operations. For more certification details, visit the QNAP Trust Center.
FAQ
Is QNAP NAS compliant with the EU CRA?
QNAP completed the first phase of its CRA compliance program on September 11, 2026, meeting the incident reporting requirements across its entire product portfolio, including NAS and networking products. QNAP is working toward full compliance by December 11, 2027, in line with EU guidance and harmonized standards.
Is a NAS a "product with digital elements" under the CRA?
Yes. A NAS is network-connected hardware that runs an operating system and applications, so it meets the CRA's definition of a product with digital elements. Routers and switches are also in scope.
How do I report a vulnerability or security incident in a QNAP product?
Report “actively exploited vulnerabilities” or “severe security incidents” through the QNAP Security Reporting Platform; QNAP PSIRT initiates its response process within 24 hours. Submit general vulnerabilities through the reporting channel on the Security Advisories page or the Security Bounty Program.
How does IEC 62443-4-1 relate to the CRA?
IEC 62443-4-1 defines requirements for a secure product development lifecycle, and its core principles closely align with the CRA's requirement for security across the entire product lifecycle. IEC 62443-4-1 verification shows that a manufacturer has the processes in place to implement the CRA's essential cybersecurity requirements.
What is an SBOM, and does the CRA require it to be public?
An SBOM (Software Bill of Materials) lists every software component and library in a product — think of it as an ingredients label for software. The CRA requires manufacturers to create an SBOM to support vulnerability handling but does not currently require it to be published; the full SBOM must be provided to authorities on request.
What is the difference between the CRA and NIS2?
The CRA governs the security of digital products and applies to manufacturers. NIS2 governs organizational cybersecurity at essential service providers in sectors such as energy, transport, and telecom. Buying CRA-compliant products lays the foundation for meeting NIS2 supply chain requirements.
Will my QNAP device continue to receive security updates?
Check your model's support period on the QNAP Product Support Status page. Products within their support period continue to receive security updates. We recommend enabling automatic updates and reviewing security advisories regularly.
Do companies outside the EU need to comply with the CRA?
Yes. Any product sold on the EU market must comply with the CRA, regardless of where the manufacturer is based. System integrators and device manufacturers can reduce their own post-market compliance burden by choosing suppliers with established SDL, PSIRT, and SBOM practices.
Belangrijkste conclusie: QNAP heeft de eerste fase van EU CRA-naleving afgerond
QNAP heeft op 11 september 2026 de eerste fase van zijn EU Cyber Resilience Act (CRA) nalevingsprogramma afgerond — dezelfde dag dat de CRA-verplichting om actief misbruikte kwetsbaarheden en ernstige incidenten te melden van kracht werd.
-
Incidentrapportage: Het QNAP Security Reporting Platform is nu live. QNAP start binnen 24 uur na ontvangst van een melding het wettelijke responsproces.
-
Veilige ontwikkeling: QNAP volgt een publiek beschikbare Secure Software Development Lifecycle (SSDLC) policy en heeft de IEC 62443-4-1 procesverificatie doorstaan.
-
Kwetsbaarhedenbeheer: QNAP PSIRT coördineert de afhandeling van kwetsbaarheden en verbindt zich ertoe extern gemelde kwetsbaarheden te verifiëren en CVE-ID's toe te wijzen binnen één week.
-
Transparantie in de toeleveringsketen: QNAP onderhoudt SBOMs in CycloneDX- en SPDX-formaten en controleert deze tegen CVE-databases en de CISA Known Exploited Vulnerabilities (KEV) catalogus.
-
Dekking: Het volledige productportfolio van QNAP, inclusief enterprise ZFS storage, zakelijke NAS, Edge AI NAS en alle netwerkproducten (routers en switches).
Wat is de EU Cyber Resilience Act (CRA)?
De EU Cyber Resilience Act (CRA), Verordening (EU) 2024/2847, vereist dat elk product met digitale elementen (PwDE) dat in de EU wordt verkocht, gedurende de gehele levenscyclus aan verplichte cybersecurity-eisen voldoet. CRA-naleving is een vereiste voor de CE-markering, en producten zonder CE-markering mogen niet op de EU-markt worden geplaatst.
Drie doelen van de CRA
- De algehele veerkracht van de EU digitale markt versterken.
- Gebruikers duidelijker inzicht geven in de beveiliging van de producten die ze kopen.
- Het aantal kwetsbaarheden in digitale producten verminderen nadat ze op de markt zijn gebracht.
Welke producten vallen onder de CRA?
De CRA dekt alle hardware of software die direct of indirect kan verbinden met een apparaat of netwerk — inclusief oplossingen voor externe gegevensverwerking. NAS-apparaten, routers, switches, besturingssystemen en applicaties vallen allemaal binnen de scope. Medische apparaten, motorvoertuigen, civiele luchtvaart en maritieme uitrusting zijn uitgesloten omdat ze al onder gelijkwaardige regelgeving vallen.
Kernverplichtingen voor alle fabrikanten onder de CRA
- Voer een cybersecurity-risicobeoordeling uit in de ontwerpfase, met toepassing van Secure by Design en Secure by Default principes.
- Stel een proces voor het afhandelen van kwetsbaarheden op dat voldoet aan de CRA-eisen.
- Lever beveiligingsupdates gedurende de ondersteuningsperiode, tot het product einde ondersteuning bereikt.
- Bereid technische documentatie voor, voltooi een conformiteitsbeoordeling en breng de CE-markering aan (geldt vanaf 11 december 2027).
- Geef duidelijke instructies voor veilig gebruik, de datum van einde ondersteuning en een contactpunt voor het melden van kwetsbaarheden.
- Meld actief misbruikte kwetsbaarheden en ernstige incidenten aan de relevante autoriteiten.
Wanneer treedt de CRA in werking? Drie belangrijke data
De CRA wordt gefaseerd ingevoerd: het melden van actief misbruikte kwetsbaarheden is verplicht vanaf 11 september 2026, en volledige naleving is vereist voor alle producten die vanaf 11 december 2027 op de EU-markt worden geplaatst.
| Datum |
Mijlpaal |
QNAP-status |
| 10 december 2024 |
CRA treedt in werking; overgangsperiode begint |
CRA-nalevingsprogramma gestart |
| 11 september 2026 |
Rapportageverplichtingen voor actief misbruikte kwetsbaarheden en ernstige incidenten gelden |
Eerste fase afgerond; Security Reporting Platform live |
| 11 december 2027 |
Deadline voor volledige naleving, inclusief conformiteitsbeoordeling en CE-markering |
Lopend, volgens EU-richtlijnen en geharmoniseerde standaarden |
Bron: Europese Commissie – Cyber Resilience Act
Hoe verschilt de CRA van NIS2, en waarom ze samen bekijken?
De CRA reguleert producten; NIS2 reguleert organisaties. Waar ze overlappen is een uniforme, risicogebaseerde strategie die de digitale toeleveringsketen beveiligt. Om als organisatie aan NIS2 te voldoen, moet de apparatuur die men koopt zelf voldoen aan de CRA.
Hoe de CRA en NIS2 samenhangen: een uniforme strategie van producten tot organisaties
|
EU CRA |
EU NIS2 Richtlijn |
| Focus |
Cybersecurity van producten met digitale elementen |
Beveiliging van netwerk- en informatiesystemen bij essentiële en belangrijke entiteiten |
| Voor wie geldt het |
Fabrikanten, importeurs en distributeurs |
Organisaties in energie, transport, telecom, gezondheidszorg, nutsbedrijven en andere sectoren |
| Verwachte uitkomst |
Veilige hardware en software met transparante componenten |
Organisatorisch cybersecuritybeleid en bescherming van kritieke infrastructuur |
| Relevantie voor QNAP |
QNAP moet direct voldoen als fabrikant |
QNAP-klanten moeten leveranciersbeveiliging beoordelen; QNAP levert verifieerbaar bewijs |
NIS2 Artikel 21(2)(d) vereist dat organisaties de beveiligingsrisico's van hun directe leveranciers en dienstverleners beoordelen. Artikel 21(2)(e) vereist beveiliging bij de aanschaf, ontwikkeling en het onderhoud van systemen, inclusief het afhandelen en openbaar maken van kwetsbaarheden. QNAP's IEC 62443-4-1 verificatie, openbaar proces voor kwetsbaarheden en afronding van de eerste fase van CRA-naleving kunnen dienen als bewijs van derden wanneer klanten hun leveranciers beoordelen.
Meer informatie: Kies QNAP-oplossingen om EU NIS2 netwerkbeveiliging en risicobeheer in de toeleveringsketen te realiseren
Hoe voldoet QNAP aan de CRA-eisen? Vier pijlers
QNAP voldoet aan de essentiële cybersecurity-eisen van de CRA via vier pijlers: een veilig ontwikkelproces geverifieerd volgens internationale standaarden, 24-uurs incidentrapportage, proactief kwetsbaarhedenbeheer en een transparante softwaretoeleveringsketen. Deze mechanismen waren al aanwezig voordat de CRA van kracht werd — het zijn geen last-minute oplossingen voor één enkele regelgeving.
Pijler 1: Een veilige ontwikkelcyclus geverifieerd volgens IEC 62443-4-1
IEC 62443-4-1 is de internationale norm van de International Electrotechnical Commission (IEC) voor veilige productontwikkelcycli. Het definieert acht veilige ontwikkelpraktijken en beoordeelt hoe goed een organisatie deze implementeert over vier volwassenheidsniveaus. QNAP heeft DEKRA's IEC 62443-4-1 procesverificatie doorstaan in september 2026. Omdat de verificatie het volledige ontwikkelproces dekt, geldt deze voor elk product dat QNAP nu en in de toekomst uitbrengt.
- Risicobeoordeling en dreigingsmodellering starten bij de eisenfase.
- Ontwerpen moeten een beveiligingsreview doorstaan, inclusief gegevensbescherming, authenticatie, toegangscontrole en encryptie.
- Ontwikkeling omvat geautomatiseerde statische (SAST) en dynamische (DAST) applicatiebeveiligingstests, aangevuld met penetratietests.
Pijler 2: CRA-conforme 24-uurs incidentrapportage
Het QNAP Security Reporting Platform dient als QNAP's centrale contactpunt voor CRA-rapportage. Klanten, eindgebruikers en security onderzoekers wereldwijd kunnen hier actief misbruikte kwetsbaarheden of ernstige beveiligingsincidenten melden. Binnen 24 uur na ontvangst van een melding start QNAP het wettelijke responsproces, beoordeelt het risico en brengt beveiligingsupdates uit.
Pijler 3: PSIRT-gestuurd kwetsbaarhedenbeheer
Het QNAP Product Security Incident Response Team (PSIRT) opereert als een commissie, met leden uit R&D, informatiebeveiliging, juridische zaken en klantenservice. QNAP volgt nieuwe kwetsbaarheden via zijn publieke Security Advisories en Security Bounty Program. Voor kwetsbaarheden gemeld door externe onderzoekers verbindt PSIRT zich ertoe verificatie te voltooien en een CVE-ID toe te wijzen binnen één week.
Pijler 4: Een transparante softwaretoeleveringsketen met SBOMs
De CRA vereist dat fabrikanten een Software Bill of Materials (SBOM) opstellen en deze op verzoek aan de autoriteiten verstrekken. QNAP onderhoudt SBOMs voor zijn NAS-software en applicaties in de industriestandaard CycloneDX- en SPDX-formaten. Het ontwikkelproces omvat Software Composition Analysis (SCA) en controleert componenten tegen CVE-databases en de Amerikaanse CISA Known Exploited Vulnerabilities (KEV) catalogus, waardoor derde partijen en open source-componenten onder risicobeheer vallen.
Gebruikerstransparantie: Duidelijk aangegeven ondersteuningsperioden
De CRA vereist dat fabrikanten het beoogde gebruik, de datum van einde ondersteuning en het contactpunt voor kwetsbaarheden melden voor elk product. Gebruikers kunnen de ondersteuningsperiode van elk model bekijken op de QNAP Product Support Status pagina en hun instellingen versterken met de NAS Security Guide.
Welke QNAP-producten vallen onder CRA-naleving?
QNAP's CRA-beveiligings- en rapportagemechanismen dekken het volledige productportfolio en worden ondersteund door meerdere onafhankelijke internationale certificeringen.
| Productcategorie |
Representatieve productlijnen |
| Enterprise storage |
ZFS storage, dual-controller NAS, all-flash NAS |
| Zakelijke en multimedia NAS |
QTS / QuTS hero zakelijke NAS, NAS voor creators en thuisgebruikers |
| AI computing |
Edge AI NAS-oplossingen |
| Netwerken |
Routers, switches |
QNAP's investering in cybersecurity is een langetermijn, systematische organisatorische capaciteit die productontwikkeling, cloudservices en operaties omvat. Voor meer certificeringsdetails, bezoek het QNAP Trust Center.
FAQ
Is QNAP NAS in overeenstemming met de EU CRA?
QNAP heeft de eerste fase van zijn CRA-nalevingsprogramma afgerond op 11 september 2026, waarmee het voldoet aan de incidentrapportage-eisen voor het volledige productportfolio, inclusief NAS en netwerkproducten. QNAP werkt toe naar volledige naleving op 11 december 2027, volgens EU-richtlijnen en geharmoniseerde standaarden.
Is een NAS een "product met digitale elementen" onder de CRA?
Ja. Een NAS is netwerkverbonden hardware die een besturingssysteem en applicaties draait, en voldoet dus aan de CRA-definitie van een product met digitale elementen. Routers en switches vallen ook binnen de scope.
Hoe meld ik een kwetsbaarheid of beveiligingsincident in een QNAP-product?
Meld "actief misbruikte kwetsbaarheden" of "ernstige beveiligingsincidenten" via het QNAP Security Reporting Platform; QNAP PSIRT start binnen 24 uur het responsproces. Meld algemene kwetsbaarheden via het meldkanaal op de Security Advisories pagina of het Security Bounty Program.
Hoe verhoudt IEC 62443-4-1 zich tot de CRA?
IEC 62443-4-1 definieert eisen voor een veilige productontwikkelcyclus, en de kernprincipes sluiten nauw aan bij de CRA-eis voor beveiliging gedurende de volledige productlevenscyclus. IEC 62443-4-1 verificatie toont aan dat een fabrikant de processen heeft om aan de essentiële cybersecurity-eisen van de CRA te voldoen.
Wat is een SBOM, en vereist de CRA dat deze openbaar is?
Een SBOM (Software Bill of Materials) bevat alle softwarecomponenten en bibliotheken in een product — zie het als een ingrediëntenlabel voor software. De CRA vereist dat fabrikanten een SBOM opstellen ter ondersteuning van kwetsbaarhedenbeheer, maar vereist momenteel niet dat deze wordt gepubliceerd; de volledige SBOM moet op verzoek aan de autoriteiten worden verstrekt.
Wat is het verschil tussen de CRA en NIS2?
De CRA regelt de beveiliging van digitale producten en geldt voor fabrikanten. NIS2 regelt organisatorische cybersecurity bij essentiële dienstverleners in sectoren zoals energie, transport en telecom. Het kopen van CRA-conforme producten legt de basis voor het voldoen aan NIS2-vereisten voor de toeleveringsketen.
Blijft mijn QNAP-apparaat beveiligingsupdates ontvangen?
Controleer de ondersteuningsperiode van uw model op de QNAP Product Support Status pagina. Producten binnen hun ondersteuningsperiode blijven beveiligingsupdates ontvangen. We raden aan automatische updates in te schakelen en regelmatig de security advisories te bekijken.
Moeten bedrijven buiten de EU voldoen aan de CRA?
Ja. Elk product dat op de EU-markt wordt verkocht moet voldoen aan de CRA, ongeacht waar de fabrikant is gevestigd. Systeemintegrators en apparaatfabrikanten kunnen hun eigen post-market nalevingslast verminderen door leveranciers te kiezen met gevestigde SDL-, PSIRT- en SBOM-praktijken.


 9 min lezen