Key Takeaway: Use ADRA NDR X to Defend Against Internal Network Threats and Make Up for What EDR Can't Do
Ransomware software can now bypass EDR (Endpoint Detection and Response), so enterprises need an additional detection mechanism that operates independently from endpoints and directly monitors internal network (LAN) traffic—this is NDR (Network Detection and Response) deployed at the network layer. Even if endpoint protection fails, attackers’ lateral movements will still be visible on the network and can be blocked in real time. QNAP ADRA NDR X enables enterprises to build this network defense chain using existing NAS and compatible switches, allowing proactive internal network detection and isolation. In addition to being license-free, it can also integrate NAS snapshots and 3-2-1-1-0 backups, creating a comprehensive data security solution that links detection, isolation, and recovery.
Cybersecurity company warning: EDR was already shut down before the threat alert was triggered
According to cybersecurity company ESET's 2026 research, around 90 EDR Killer tools have been tracked in the market, among which 54 exploit BYOVD (Bring Your Own Vulnerable Driver) technology to gain system kernel privileges and directly terminate endpoint protection programs.
Behind the statistics of these 90 tools lies a commercialized attack supply chain. ESET further exposed the ransomware-as-a-service (RaaS) group Gentlemen, which provides attackers with an EDR Killer tool called GentleKiller: GentleKiller has at least 8 variants, disguises itself as legitimate software such as Kaspersky and Valorant, and can precisely target more than 48 security products, covering over 400 processes. The toolkit even includes third-party tools like HexKiller, ThrottleBlood, and HavocKiller as substitutes.
What's even more sophisticated is the attack method itself. BYOVD attacks load drivers that are 'legitimately signed but vulnerable.' The operating system allows them, enabling attackers to escalate privileges to kernel level, forcibly terminate EDR engines, log collection, and monitoring services. Throughout the entire process, endpoint protection may not even issue a final alert.
Why Relying Solely on EDR Is Not Enough for Protection
Therefore, this attack exposes not a vulnerability in a single EDR, but rather a structural single point of dependency. Endpoint detection assumes that the agent is still running properly, and the EDR Killer attack specifically targets this assumption. In addition, there are deployments where the agent simply cannot be installed, such as IP cameras, printers, IoTunit devices, legacy systems, external visitor laptops, etc. The conclusion in the U.S. CISA Red Team Exercise Report is quite direct: critical infrastructure organizations being tested are “overly reliant on host-based EDR and lack sufficient network-layer defenses.”
Once EDR is bypassed and there is no corresponding detection mechanism in the intranet, attackers essentially gain unrestricted internal access: lateral movement, scanning other unit, establishing connections, infiltrating and spreading, exfiltrating data, all without anyone noticing.
Therefore, enterprises need to deploy threat detection and response mechanisms at the network layer, such as NDR, to truly block attackers' actions. NDR identifies anomalies by analyzing internal network traffic behavior, without relying on any endpoint agents. Its value lies in being "out-of-band": it does not depend on any potentially compromised host, but observes east-west traffic at the network layer from the switch, comparing abnormal connection behaviors, detecting lateral movement, and suspicious C2 communications. Even if EDR is bypassed by GentleKiller, traces of encrypted activities on the network remain visible.
QNAP ADRA NDR X: Make QNAP NAS the proactive cybersecurity brain
Traditional NDR solutions often mean dedicated hardware plus annual licenses priced by traffic, causing SMBs to back out at the quoting stage. QNAP ADRA NDR X does things differently: users can directly download and install it for free from App Center onto supported QNAP NAS (QTS/QuTS hero 5.2 or above), pair it with a compatible QNAP switch, and instantly upgrade their existing unit to an NDR internal threat detection center—no license fees required.
In the face of the EDR Killer scenario, ADRA NDR X's defense mechanism is divided into three layers:
-
Active Threat Trap (Threat Watch & Trap): Simulates common services such as SSH and SAMBA as honeypots, proactively luring malicious programs exploring the intranet. Selectively encapsulates detection instead of full traffic analysis, ensuring no network slowdown.
-
Lateral movement detection and deep threat analysis: Identifies abnormal intranet connections and unit behaviors, maps threat events to the MITRE ATT&CK® framework, and uses AI event analysis reports to automatically generate event summaries, infection path visualization, and remediation recommendations, so IT staff do not need to read logs one by one.
-
Automatic isolation response: When high-risk unit is detected, it can automatically isolate the unit, providing four levels of protection from “notification only” to automatic lockdown, preventing spread without interrupting the entire network operation.
QNAP ADRA NDR X adopts an agentless design, allowing enterprise IT to deploy quickly without having to install software on every employee's computer. It operates without impacting network performance and does not affect daily operations, ensuring that all connected endpoints unit receive comprehensive security protection. In addition, the solution integrates dual reporting of “single event AI intelligent threat analysis” and “overall internal network security overview,” helping IT staff accurately transform security data into actionable key insights, fully grasp the enterprise's security posture, and respond efficiently in real time.
ADRA NDR X vs EDR Key Comparison
| Comparison Items |
QNAP ADRA NDR X |
EDR |
| Detects data source |
Network packets and suspicious activities of lateral movement within the intranet |
Data from single endpoint deployment |
| Unmanaged unit protection |
Comprehensive coverage. No need to install Agent, fully protects IoT, OT, and BYOD. |
Unable to cover. Unmanaged unit without Agent installation is completely invisible. |
| Resistance to being shut down and anti-tampering capability |
is extremely high. It operates independently from the computer, so even if the computer is infected, it cannot be disabled. |
is relatively weaker. Once elevated privileges are obtained, it is easily shut down by hackers or the Agent is disabled. |
| License fee model |
No license fee. No limit on the number of installations, suitable for unit enterprises with many users. |
Fees are calculated based on the number of endpoints. Charged per device, the more unit you have, the higher the linear cost growth. |
| Deployment and Maintenance Costs |
Low cost, zero disruption. Only need to set up traffic mirroring, no need to access endpoint computers. |
High cost, complex maintenance. Requires deploying software on each device and handling software conflicts and strategy adjustments. |
| Regulatory Compliance (NIST CSF 2.0 / NIS2) |
Compliant. Meets the mandatory requirements for “continuous network monitoring.” |
Requires integration with other tools. Only provides endpoint logs and cannot independently meet network layer compliance. |
The Ultimate Insurance for Data Security: Immutable Snapshots and 3-2-1 Backup
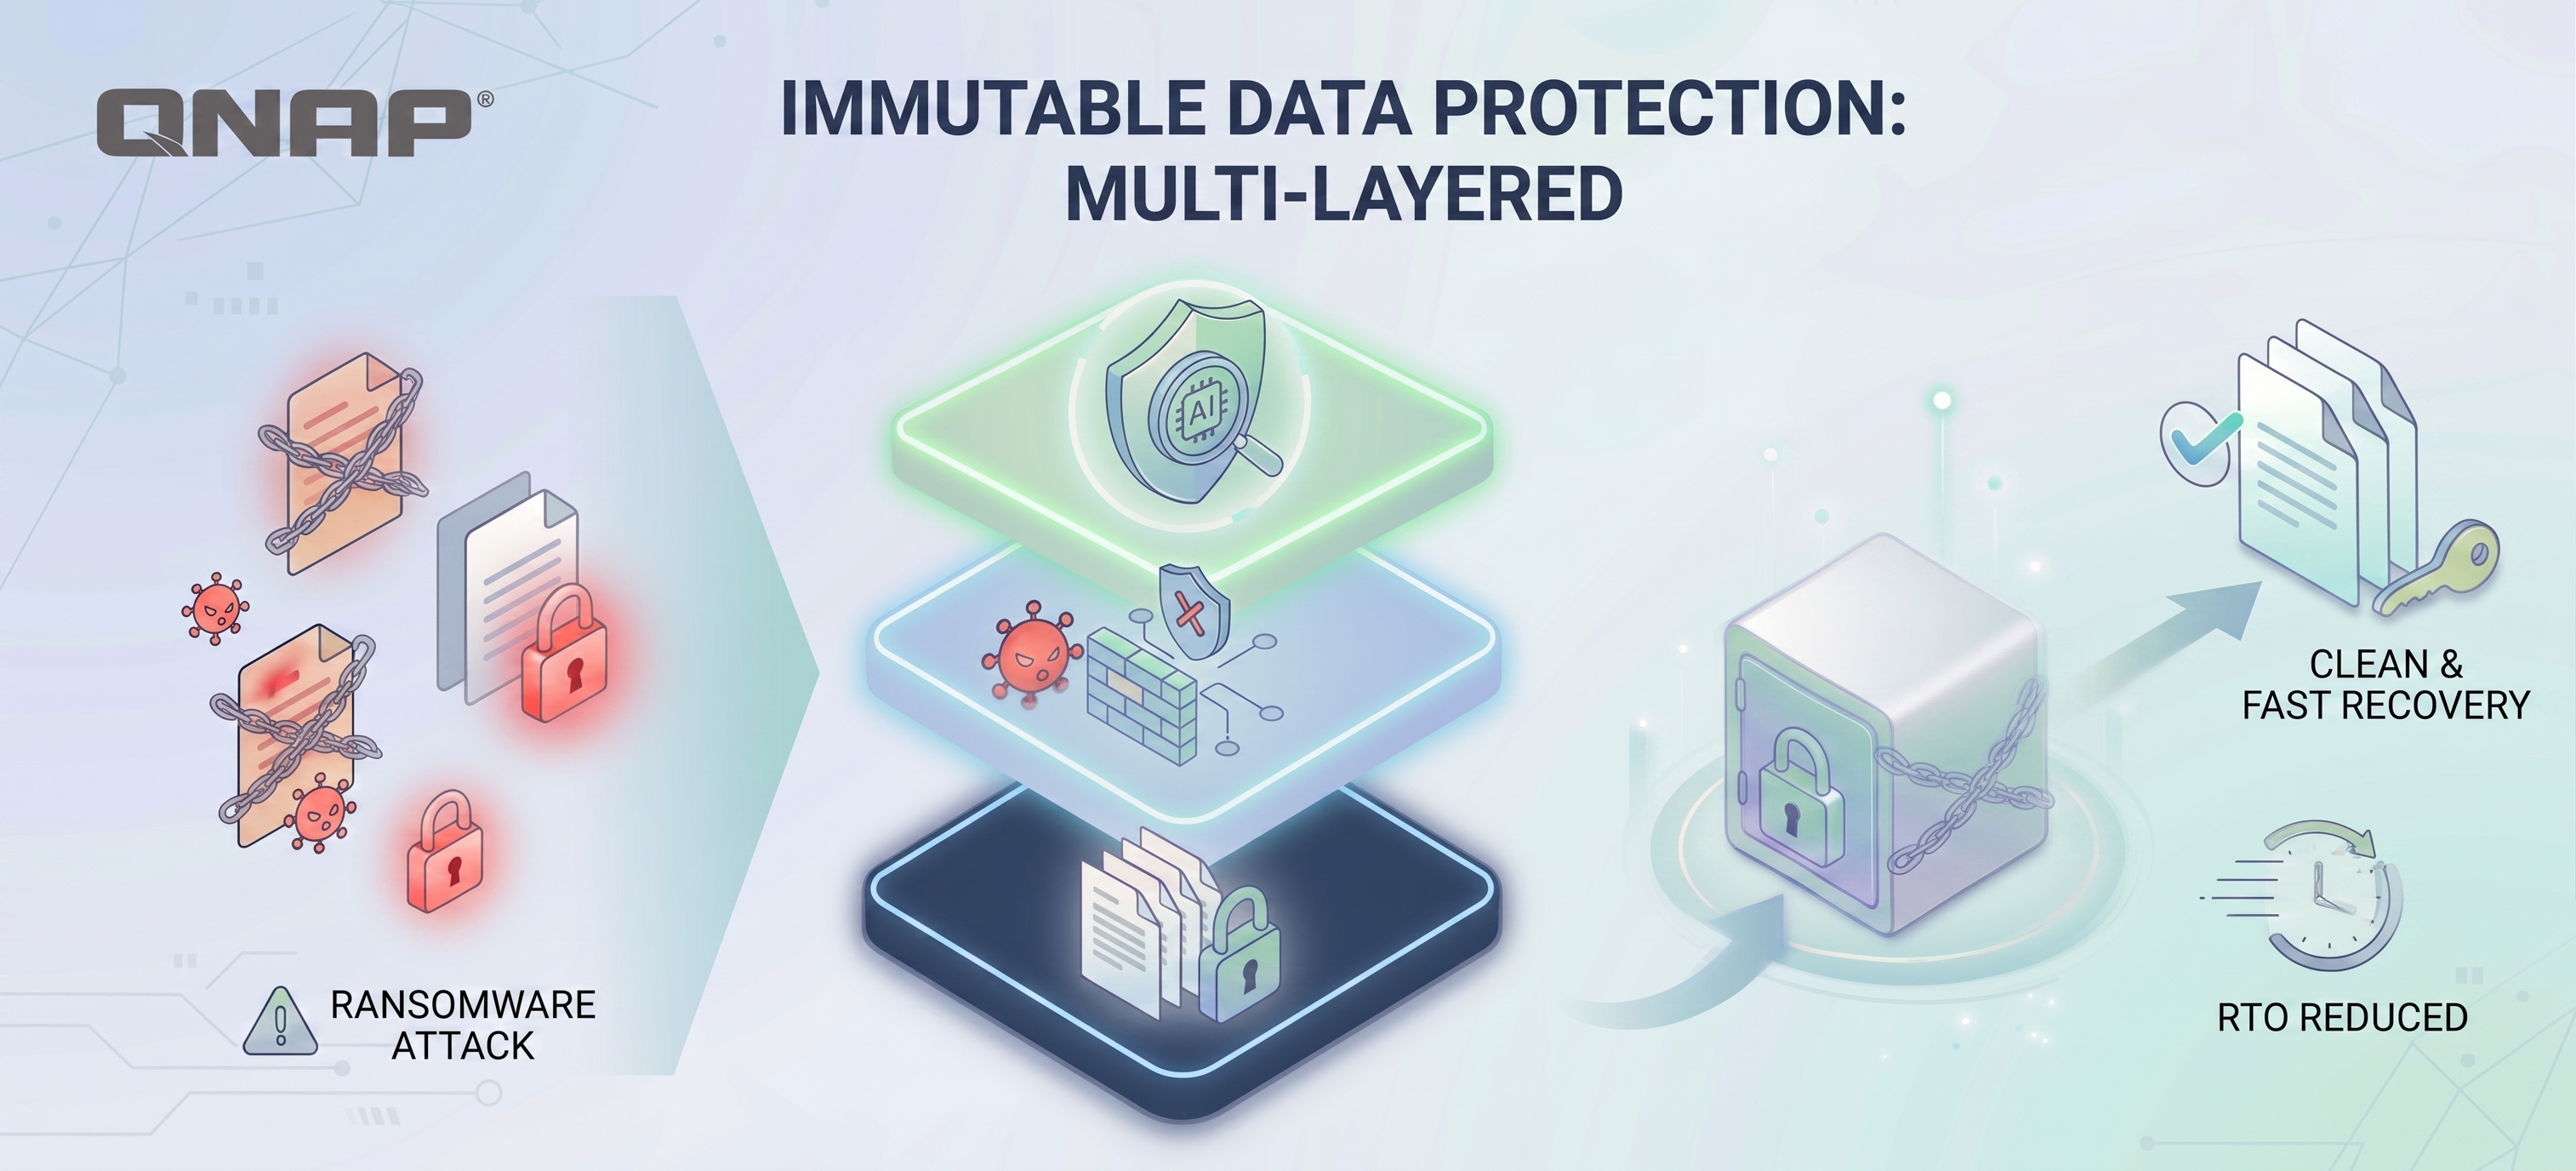
However, enterprises should note that no detection layer can guarantee 100% interception, especially as threats become more complex in the AI era. ADRA NDR X can be integrated with QNAP's NAS snapshot technology to restore data to its intact state before infection after threat isolation. By following the 3-2-1-1-0 backup principle (3 copies of data, 2 types of media, 1 offsite copy, 1 offline/immutable copy, 0 errors), even when facing threats, enterprises can still retain a clean backup that attackers cannot encrypt or tamper with, creating a comprehensive data security solution.
Extension Read more: Ransomware Survival Guide: Why are “Immutability” and “Offline Backup” the last line of defense for enterprises in 2026?
FAQ (FAQ)
What is EDR Killer? Why can't antivirus software block it?
EDR Killer is a specialized attack tool targeting endpoint protection, often leveraging BYOVD technology to load vulnerable drivers with valid signatures, forcibly terminating security software programs after obtaining kernel privileges. Because the drivers are legally signed, operating systems and antivirus engines often treat them as legitimate components and allow them to run.
Already have EDR, do you still need NDR?
Yes, you do. Both cover different stages of the attack chain: EDR excels at blocking execution and persistence on endpoints, while NDR specializes in detecting lateral movement, C2 communications, and data exfiltration. NDR is deployed at the network layer and won't be affected if the main host is shut down, making it a reliable external detection source when EDR is compromised. For example, QNAP is one of the security service providers offering NDR solutions, helping enterprises monitor internal packet and traffic anomalies and precisely block high-risk behaviors and deployments without changing their existing network infrastructure.
Does ADRA NDR X require an additional license?
No. ADRA NDR X can be downloaded for free from App Center and installed on supported QNAP NAS. When used with compatible QNAP switches, there is no need to pay extra license fees.
Punto chiave: usa ADRA NDR X per difenderti dalle minacce interne alla rete e colmare le lacune dell’EDR
I software ransomware ora possono bypassare l’EDR (Endpoint Detection and Response), quindi le aziende hanno bisogno di un meccanismo di rilevamento aggiuntivo che operi in modo indipendente dagli endpoint e monitori direttamente il traffico della rete interna (LAN): questa è la funzione dell’NDR (Network Detection and Response) implementato a livello di rete. Anche se la protezione degli endpoint fallisce, i movimenti laterali degli attaccanti saranno comunque visibili sulla rete e potranno essere bloccati in tempo reale. QNAP ADRA NDR X consente alle aziende di costruire questa catena di difesa di rete utilizzando NAS esistenti e switch compatibili, permettendo il rilevamento e l’isolamento proattivo delle minacce interne. Oltre a essere senza licenza, può anche integrare snapshot NAS e backup 3-2-1-1-0, creando una soluzione completa di sicurezza dei dati che collega rilevamento, isolamento e ripristino.
Avvertimento delle aziende di cybersecurity: l’EDR era già stato disattivato prima che venisse generato l’allarme
Secondo la ricerca 2026 della società di sicurezza informatica ESET, sono stati tracciati circa 90 strumenti EDR Killer sul mercato, di cui 54 sfruttano la tecnologia BYOVD (Bring Your Own Vulnerable Driver) per ottenere privilegi di kernel di sistema e terminare direttamente i programmi di protezione degli endpoint.
Dietro le statistiche di questi 90 strumenti si cela una supply chain di attacco commercializzata. ESET ha inoltre rivelato il gruppo ransomware-as-a-service (RaaS) Gentlemen, che fornisce agli attaccanti uno strumento EDR Killer chiamato GentleKiller: GentleKiller ha almeno 8 varianti, si maschera da software legittimo come Kaspersky e Valorant, e può colpire con precisione oltre 48 prodotti di sicurezza, coprendo più di 400 processi. Il toolkit include anche strumenti di terze parti come HexKiller, ThrottleBlood e HavocKiller come alternative.
Ancora più sofisticato è il metodo di attacco stesso. Gli attacchi BYOVD caricano driver "firmati legittimamente ma vulnerabili". Il sistema operativo li consente, permettendo agli attaccanti di ottenere privilegi a livello kernel, terminare forzatamente i motori EDR, la raccolta dei log e i servizi di monitoraggio. Durante tutto il processo, la protezione endpoint potrebbe non emettere nemmeno un avviso finale.
Perché affidarsi solo all’EDR non basta per la protezione
Quindi, questo attacco non rivela una vulnerabilità di un singolo EDR, ma piuttosto una dipendenza strutturale da un unico punto. Il rilevamento endpoint presuppone che l’agente sia ancora in esecuzione correttamente, e l’attacco EDR Killer mira proprio a questa assunzione. Inoltre, ci sono scenari in cui l’agente non può essere installato, come telecamere IP, stampanti, dispositivi IoTunit, sistemi legacy, laptop di visitatori esterni, ecc. La conclusione del Rapporto sull’esercitazione Red Team della CISA USA è piuttosto diretta: le organizzazioni di infrastrutture critiche testate sono "eccessivamente dipendenti dall’EDR host-based e mancano di adeguate difese a livello di rete".
Una volta che l’EDR viene bypassato e non esiste un meccanismo di rilevamento corrispondente nell’intranet, gli attaccanti ottengono di fatto accesso interno illimitato: movimento laterale, scansione di altri unit, stabilire connessioni, infiltrarsi e diffondersi, esfiltrare dati, tutto senza che nessuno se ne accorga.
Pertanto, le aziende devono implementare meccanismi di rilevamento e risposta alle minacce a livello di rete, come l’NDR, per bloccare davvero le azioni degli attaccanti. L’NDR identifica le anomalie analizzando il comportamento del traffico della rete interna, senza dipendere da alcun agente endpoint. Il suo valore sta nell’essere "out-of-band": non dipende da nessun host potenzialmente compromesso, ma osserva il traffico est-ovest a livello di switch, confrontando comportamenti di connessione anomali, rilevando movimenti laterali e comunicazioni C2 sospette. Anche se l’EDR viene bypassato da GentleKiller, le tracce delle attività cifrate sulla rete restano visibili.
QNAP ADRA NDR X: trasforma il NAS QNAP nel cervello proattivo della cybersecurity
Le soluzioni NDR tradizionali spesso richiedono hardware dedicato e licenze annuali calcolate in base al traffico, scoraggiando le PMI già in fase di preventivo. QNAP ADRA NDR X fa le cose diversamente: gli utenti possono scaricarlo e installarlo gratuitamente da App Center su NAS QNAP supportati (QTS/QuTS hero 5.2 o superiore), abbinarlo a uno switch QNAP compatibile e aggiornare istantaneamente la propria unit esistente a un centro di rilevamento minacce interne NDR—senza costi di licenza.
Di fronte allo scenario EDR Killer, il meccanismo di difesa di ADRA NDR X si articola su tre livelli:
-
Active Threat Trap (Threat Watch & Trap): simula servizi comuni come SSH e SAMBA come honeypot, attirando proattivamente i programmi malevoli che esplorano l’intranet. Incapsula selettivamente il rilevamento invece di analizzare tutto il traffico, garantendo nessun rallentamento della rete.
-
Rilevamento movimento laterale e analisi approfondita delle minacce: identifica connessioni anomale e comportamenti delle unit nella rete interna, mappa gli eventi di minaccia al framework MITRE ATT&CK®, e utilizza report di analisi eventi AI per generare automaticamente riepiloghi, visualizzazione dei percorsi di infezione e raccomandazioni di remediation, così il personale IT non deve leggere i log uno per uno.
-
Risposta di isolamento automatica: quando viene rilevata una unit ad alto rischio, può isolarla automaticamente, offrendo quattro livelli di protezione da "solo notifica" a blocco automatico, prevenendo la diffusione senza interrompere l’intera operatività di rete.
QNAP ADRA NDR X adotta un design senza agent, consentendo all’IT aziendale di implementare rapidamente senza dover installare software su ogni computer dei dipendenti. Funziona senza impattare le prestazioni di rete e non influenza le operazioni quotidiane, garantendo che tutte le unit endpoint connesse ricevano una protezione di sicurezza completa. Inoltre, la soluzione integra la doppia reportistica di "analisi intelligente AI di singolo evento" e "panoramica della sicurezza della rete interna", aiutando il personale IT a trasformare con precisione i dati di sicurezza in insight chiave azionabili, comprendere pienamente la postura di sicurezza aziendale e rispondere in modo efficiente in tempo reale.
Confronto chiave ADRA NDR X vs EDR
| Elementi di confronto |
QNAP ADRA NDR X |
EDR |
| Fonte dati rilevata |
Pacchetti di rete e attività sospette di movimento laterale nell’intranet |
Dati da singolo endpoint |
| Protezione unit non gestite |
Copertura completa. Nessun bisogno di installare Agent, protegge completamente IoT, OT e BYOD. |
Non copre. Le unit non gestite senza Agent sono completamente invisibili. |
| Resistenza alla disattivazione e capacità anti-manomissione |
è estremamente elevata. Opera indipendentemente dal computer, quindi anche se il computer è infetto, non può essere disabilitato. |
è relativamente più debole. Una volta ottenuti privilegi elevati, può essere facilmente disattivato dagli hacker o l’Agent viene disabilitato. |
| Modello di licenza |
Nessun costo di licenza. Nessun limite al numero di installazioni, adatto a unit aziendali con molti utenti. |
I costi sono calcolati in base al numero di endpoint. Addebitato per dispositivo, più unit hai, maggiore è la crescita lineare dei costi. |
| Costi di implementazione e manutenzione |
Basso costo, zero interruzioni. Basta impostare il mirroring del traffico, senza accedere ai computer endpoint. |
Costo elevato, manutenzione complessa. Richiede l’installazione del software su ogni dispositivo e la gestione di conflitti software e aggiustamenti di policy. |
| Conformità normativa (NIST CSF 2.0 / NIS2) |
Conforme. Soddisfa i requisiti obbligatori di "monitoraggio continuo della rete". |
Richiede integrazione con altri strumenti. Fornisce solo log endpoint e non può soddisfare autonomamente la conformità a livello di rete. |
L’assicurazione definitiva per la sicurezza dei dati: snapshot immutabili e backup 3-2-1
Tuttavia, le aziende devono ricordare che nessun livello di rilevamento può garantire l’intercettazione al 100%, soprattutto con minacce sempre più complesse nell’era dell’AI. ADRA NDR X può essere integrato con la tecnologia snapshot NAS di QNAP per ripristinare i dati al loro stato integro prima dell’infezione dopo l’isolamento della minaccia. Seguendo il principio di backup 3-2-1-1-0 (3 copie dei dati, 2 tipi di supporto, 1 copia offsite, 1 copia offline/immutabile, 0 errori), anche di fronte alle minacce, le aziende possono comunque conservare un backup pulito che gli attaccanti non possono cifrare o manomettere, creando una soluzione completa di sicurezza dei dati.
Lettura di approfondimento: Guida alla sopravvivenza al ransomware: perché “Immutabilità” e “Backup offline” sono l’ultima linea di difesa per le aziende nel 2026?
FAQ (Domande frequenti)
Cos’è un EDR Killer? Perché l’antivirus non può bloccarlo?
EDR Killer è uno strumento di attacco specializzato che prende di mira la protezione degli endpoint, spesso sfruttando la tecnologia BYOVD per caricare driver vulnerabili con firme valide, terminando forzatamente i programmi di sicurezza dopo aver ottenuto privilegi kernel. Poiché i driver sono firmati legalmente, i sistemi operativi e i motori antivirus spesso li trattano come componenti legittimi e ne consentono l’esecuzione.
Ho già EDR, serve comunque l’NDR?
Sì, serve. Coprono fasi diverse della catena di attacco: l’EDR è eccellente nel bloccare l’esecuzione e la persistenza sugli endpoint, mentre l’NDR è specializzato nel rilevare movimenti laterali, comunicazioni C2 ed esfiltrazione dati. L’NDR è implementato a livello di rete e non viene influenzato se l’host principale viene spento, diventando una fonte di rilevamento esterna affidabile quando l’EDR è compromesso. Ad esempio, QNAP è uno dei fornitori di servizi di sicurezza che offre soluzioni NDR, aiutando le aziende a monitorare pacchetti e anomalie di traffico interni e bloccare con precisione comportamenti e deployment ad alto rischio senza modificare l’infrastruttura di rete esistente.
ADRA NDR X richiede una licenza aggiuntiva?
No. ADRA NDR X può essere scaricato gratuitamente da App Center e installato su NAS QNAP supportati. Se utilizzato con switch QNAP compatibili, non è necessario pagare costi di licenza aggiuntivi.


 8 min di lettura