Applicable products
- QNAP NAS running Plex Media Server 1.43.2 or earlier.
Overview
Plex2Shell refers to four vulnerabilities in the third-party application Plex Media Server, affecting version 1.43.2 and earlier: CVE-2026-96652, CVE-2026-96654, CVE-2026-96655, and CVE-2026-96656. Each presents limited risk on its own, but chained together they allow an unauthenticated remote attacker to execute arbitrary code with the privileges of the Plex Media Server process.
According to Plex, a public proof of concept was released on October 16, and internet-facing servers that have not been updated have since been subject to widespread attacks. Compromised servers have been used to run cryptocurrency miners and proxy software.
The fixed release, Plex Media Server 1.43.3 (build 1.43.3.10861 and later), is available in the QNAP App Center. The vulnerabilities reside in Plex Media Server only; QNAP operating systems such as QTS and QuTS hero are not themselves affected.
Important: If Plex on your NAS was reachable from the Internet while running 1.43.2 or earlier, updating alone is not enough. Treat the NAS as potentially compromised and complete the clean reinstall, compromise check, and credential reset described below.
Q1. Is my NAS affected?
Only a NAS with Plex Media Server 1.43.2 or earlier installed is affected. QNAP operating systems are not themselves affected, and a NAS without Plex needs no action.
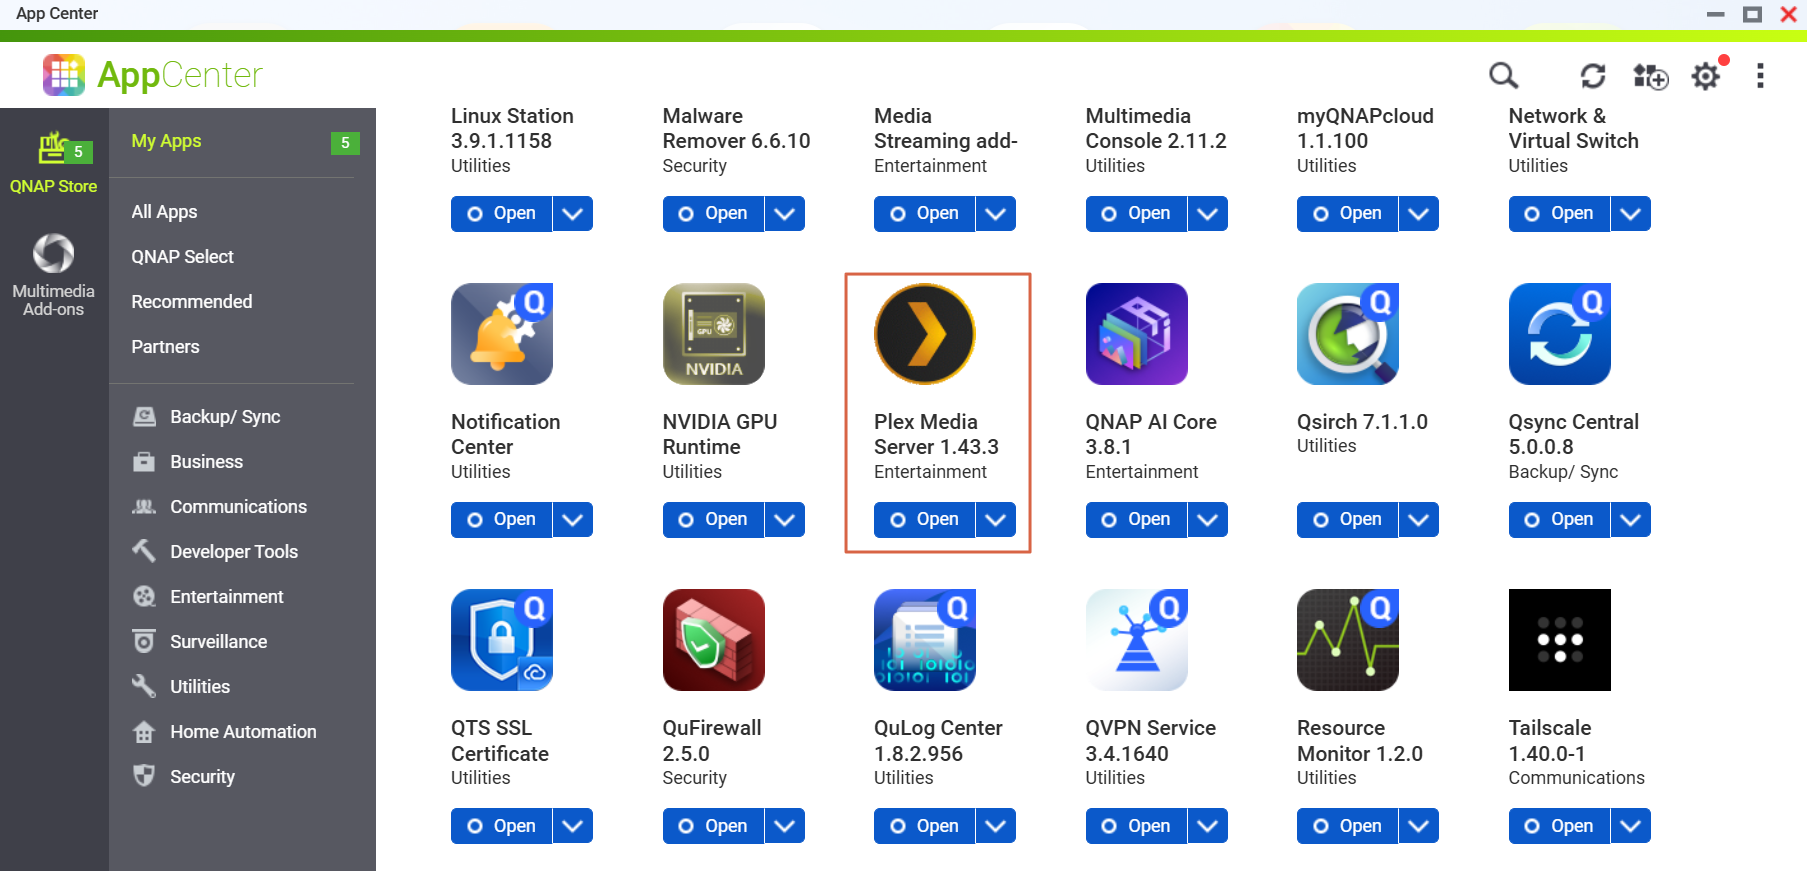
To check the version:
- App Center > My Apps shows 1.43.3 for the patched release.
Q2. How do I know whether my Plex was reachable from the Internet?
If any of the following applied while you were running 1.43.2 or earlier, or if you upgraded to a non-affected version only after the PoC was publicly disclosed on October 16, treat the NAS as potentially compromised and complete Q4 to Q8:
- Remote Access was enabled in Plex Web > Settings > Remote Access;
- your router forwards port 32400;
- UPnP is enabled on your router and Plex Remote Access was enabled (Plex opens the port automatically);
- Plex was exposed through myQNAPcloud auto router configuration or any other means.
Q3. How do I update?
- Go to App Center > My Apps > Plex Media Server > Update.
- Confirm that the version is 1.43.3. or later.
If no update is shown, refresh App Center and make sure the NAS can reach the Internet.
Later Plex releases (with other security fixes) will also be published once verified; update again when they appear, but do not wait for them – update now.
Q4. I have updated. Is there anything else to do?
- If Plex was never reachable from the Internet: updating is enough; we still recommend the exposure-reduction settings in Q7.
- If it was reachable: updating only closes the entry point and does not remove anything already installed. Complete Q5 (clean reinstall), Q6 (indicators of compromise), and Q8 (credential reset), in that order.
Q5. How do I perform a clean reinstall?
- If you would like QNAP to help confirm a compromise, first copy the Plex Logs folder (under "Plex Media Server" in the PlexData shared folder) to another location.
- Go to App Center > My Apps > Plex Media Server and select Remove.
- Use File Station to check whether a "Plex Media Server" folder still exists in the PlexData shared folder. If it does, do not reuse it: at minimum delete everything in the Codecs folder and review Preferences.xml for transcoder-related options you did not set.
- Reinstall 1.43.3 or later from App Center.
- After reinstalling, do not restore the previous contents of the Codecs folder. Plex will download the components it needs.
Q6. How do I check for indicators of compromise?
Look for any of the following:
- Unknown processes started by Plex Media Server, in particular names such as
myawesomeproxy, mylovelyminer, or x12345;
- unfamiliar
.so or .dll files in the Codecs folder;
- outbound connections to
proxystream.st;
- sustained high CPU usage while nothing is playing (see Resource Monitor);
- a Malware Remover detection (for example, detection code MR2104).
If you find any of these, do not just remove the suspicious program; other components or persistence mechanisms may remain. Complete the clean reinstall in Q5 and the credential reset in Q8. If you need QNAP's help, preserve the Logs folder first and open a case with Technical Support.
Q7. How do I reduce exposure?
- Disable Remote Access in Plex Web > Settings > Remote Access if you do not need it;
- remove the port 32400 forwarding rule on your router and disable UPnP; remove any myQNAPcloud auto router configuration for Plex;
- use a VPN (for example, QVPN Service on the NAS) when you need remote access;
- keep QTS or QuTS hero and all apps up to date, and enable Malware Remover scheduled scans and QuFirewall;
- if your device is beyond its software support period and cannot run the latest operating system, review its overall security posture as well.
Q8. Which credentials should I reset?
- Plex account: sign out all devices in your Plex account settings first, then change your Plex password. Because the administrator token may have been exposed, changing the password alone is not enough.
- NAS accounts: shared folders that Plex Media Server could access, and credentials stored on the NAS, should be treated as potentially exposed. Change the NAS administrator and user passwords, enable two-step verification, and rotate passwords or access keys stored by other services on the NAS (for example, backup jobs and cloud connections).
Q9. Will later Plex versions be published? Should I wait?
Later Plex releases will be published in App Center once verified; they contain other security fixes. Version 1.43.3 already fixes Plex2Shell, so do not wait.
Q10. How do I get help from QNAP?
Open a case with QNAP Technical Support and include your Plex version, whether Plex was reachable from the Internet, and any indicators you found. If you want QNAP to help confirm a compromise, preserve the Logs folder before removing Plex.
Further Reading
적용되는 제품
- Plex Media Server 1.43.2 또는 이전 버전을 실행하는 QNAP NAS.
개요
Plex2Shell은 타사 애플리케이션 Plex Media Server의 네 가지 취약점을 나타내며, 버전1.43.2 및 이전에 영향을 미칩니다: CVE-2026-96652, CVE-2026-96654, CVE-2026-96655, 그리고CVE-2026-96656. 각각은 자체적으로 제한된 위험을 나타내지만, 함께 연결되면인증되지 않은 원격 공격자가 임의의 코드를 실행할 수 있게 합니다.
Plex에 따르면, 10월 16일에 공개 개념 증명이 발표되었으며, 업데이트되지 않은 인터넷에 노출된 서버는 이후 광범위한 공격의 대상이 되었습니다. 손상된 서버는 암호화폐 채굴기와 프록시 소프트웨어를 실행하는 데 사용되었습니다.
수정된 릴리스, Plex Media Server 1.43.3 (빌드 1.43.3.10861 및 이후)는 QNAP App Center에서 사용할 수 있습니다. 취약점은 Plex Media Server에만 존재하며, QTS 및QuTS hero와 같은 QNAP 운영 체제는 영향을 받지 않습니다.
중요: NAS의 Plex가 1.43.2 또는 이전 버전으로 실행되는 동안 인터넷에서 접근 가능했다면, 업데이트만으로는충분하지 않습니다. NAS가 손상되었을 가능성을 고려하고 아래에 설명된 대로 깨끗한 재설치, 손상 여부 확인 및 자격 증명 재설정을 완료하십시오.
Q1. 내 NAS가 영향을 받습니까?
Plex Media Server 1.43.2 또는 이전 버전이 설치된 NAS만 영향을 받습니다. QNAP 운영 체제 자체는 영향을 받지 않으며, Plex가 없는 NAS는 조치가 필요 없습니다.
버전을 확인하려면:
- App Center > My Apps에서 패치된 릴리스의1.43.3을(를) 표시합니다.
Q2. 내 Plex가 인터넷에서 접근 가능했는지 어떻게 알 수 있습니까?
다음 중 하나가1.43.2 또는 이전 버전을 실행하는 동안 적용되었거나, 10월 16일에 PoC가 공개된 후에만 비영향 버전으로 업그레이드한 경우, NAS가 잠재적으로 손상된 것으로 간주하고 Q4에서 Q8을 완료하십시오:
- Plex Web > Settings > Remote Access에서 원격 액세스가 활성화되었습니다;
- 라우터가 포트32400을(를) 포워딩합니다;
- 라우터에서 UPnP가 활성화되어 있고 Plex 원격 액세스가 활성화되었습니다(Plex가 포트를 자동으로 엽니다);
- Plex가 myQNAPcloud 자동 라우터 구성또는 다른 방법을 통해 노출되었습니다.
Q3. 어떻게 업데이트합니까?
- App Center > My Apps > Plex Media Server > Update로 이동합니다.
- 버전이1.43.3. 이상인지 확인하십시오.
업데이트가 표시되지 않으면, App Center을 새로고침하고 NAS가 인터넷에 연결되어 있는지 확인하십시오.
추후 Plex 릴리스(다른 보안 수정 포함)도 검증 후 게시될 예정입니다. 업데이트가 나타나면 다시 업데이트하십시오. 그러나기다리지 말고 지금 업데이트하십시오.
Q4. 업데이트를 완료했습니다. 추가로 해야 할 일이 있습니까?
- Plex가 인터넷에서 접근할 수 없었던 경우:업데이트만으로 충분합니다. 그러나 Q7의 노출 감소 설정을 권장합니다.
- 접근 가능했던 경우:업데이트는 진입점을 닫을 뿐 이미 설치된 것을 제거하지 않습니다. Q5 (깨끗한 재설치), Q6 (침해 지표), Q8 (자격 증명 재설정)을 순서대로 완료하십시오.
Q5. 깨끗한 재설치는 어떻게 수행합니까?
- QNAP이 침해 여부를 확인하는 데 도움을 원하시면, 먼저 Plex Logs폴더("Plex Media Server"의PlexData공유 폴더 내)를 다른 위치로 복사하십시오.
- App Center > 내 앱 > Plex Media Server로 이동하여제거를 선택하십시오.
- File Station을(를) 사용하여 "Plex Media Server" 폴더가PlexData공유 폴더에 여전히 존재하는지 확인합니다. 존재할 경우, 재사용하지 마십시오: 최소한Codecs폴더의 모든 내용을 삭제하고, 설정하지 않은 트랜스코더 관련 옵션을 위해Preferences.xml을(를) 검토하십시오.
- App Center에서1.43.3 이상을(를) 다시 설치합니다.
- 재설치 후, Codecs 폴더의 이전 내용을복원하지 마십시오. Plex는 필요한 구성 요소를 다운로드할 것입니다.
Q6. 침해 지표를 어떻게 확인합니까?
다음 중 하나를 찾습니다:
- Plex Media Server에 의해 시작된 알 수 없는 프로세스, 특히
myawesomeproxy, mylovelyminer, 또는x12345와 같은 이름;
- Codecs폴더에 있는 낯선
.so또는.dll파일;
proxystream.st로의 아웃바운드 연결;- 아무것도 재생되지 않을 때 지속적으로 높은 CPU 사용량(참조: 리소스 모니터);
- Malware Remover 탐지(예: 탐지 코드MR2104).
이 중 하나라도 발견되면, 의심스러운 프로그램을단순히 제거하지 마십시오; 다른 구성 요소나 지속성 메커니즘이 남아 있을 수 있습니다. Q5의 완전한 재설치와 Q8의 자격 증명 재설정을 완료하십시오. QNAP의 도움이 필요하다면, 먼저 Logs 폴더를 보존하고 기술 지원에 케이스를 열어주십시오.
Q7. 노출을 어떻게 줄입니까?
- 필요하지 않다면Plex Web > Settings > Remote Access에서 원격 액세스를 비활성화하십시오;
- 라우터에서 포트 32400 포워딩 규칙을 제거하고 UPnP를 비활성화하십시오; Plex를 위한 myQNAPcloud 자동 라우터 구성을(를) 제거하십시오;
- 원격 액세스가 필요할 때는 VPN(예: NAS에서의QVPN Service)을 사용하십시오;
- QTS 또는QuTS hero및 모든 앱을 최신 상태로 유지하고, Malware Remover 예약 스캔 및 QuFirewall을 활성화하십시오;
- 기기가 소프트웨어 지원 기간을 초과하여 최신 운영 체제를 실행할 수 없는 경우, 전체적인 보안 상태도 검토하십시오.
Q8. 어떤 자격 증명을 재설정해야 합니까?
- Plex 계정:먼저 Plex 계정 설정에서 모든 기기에서 로그아웃한 후 Plex 비밀번호를 변경하십시오. 관리자토큰이 노출되었을 수 있으므로 비밀번호만 변경하는 것으로는 충분하지 않습니다.
- NAS 계정: Plex Media Server가 접근할 수 있는 공유 폴더와 NAS에 저장된 자격 증명은 잠재적으로 노출된 것으로 간주해야 합니다. NAS 관리자및 사용자 비밀번호를 변경하고, 2단계 인증을 활성화하며, NAS에 저장된 다른 서비스의 비밀번호나 액세스 키(예: 백업 작업 및 클라우드 연결)를 교체하십시오.
Q9. 나중에 Plex 버전이 출시될까요? 기다려야 하나요?
나중에 출시될 Plex 버전은App Center에서 검증 후 게시될 예정이며, 다른 보안 수정 사항을 포함하고 있습니다. 버전1.43.3은 이미 Plex2Shell을 수정하였으므로 기다리지 마십시오.
Q10. QNAP에서 어떻게 도움을 받을 수 있습니까?
QNAP 기술 지원에 케이스를 열고 Plex 버전, Plex가 인터넷에서 접근 가능했는지 여부 및 발견한 지표를 포함하십시오. QNAP이 침해 여부를 확인하는 데 도움을 원하시면, Plex를 제거하기 전에 Logs 폴더를 보존하십시오.
추가 읽기


