The eight categories correspond to QNAP's alignment with ISO/IEC 27002:2022 technical and organizational controls. Each card indicates the corresponding Annex A control number.

A.5.15–A.5.18・A.8.2・A.8.5
Identity and Access Control
- AD/LDAP domain integration, centralized account management
- Two-factor authentication (2FA/2SV) can be enforced for specified accounts
- Delegated administration—minimum privilege granted according to duties QTShero
- Shared data folder and file-level ACL permission management
- Password policy enforcement, auto logout after idle period
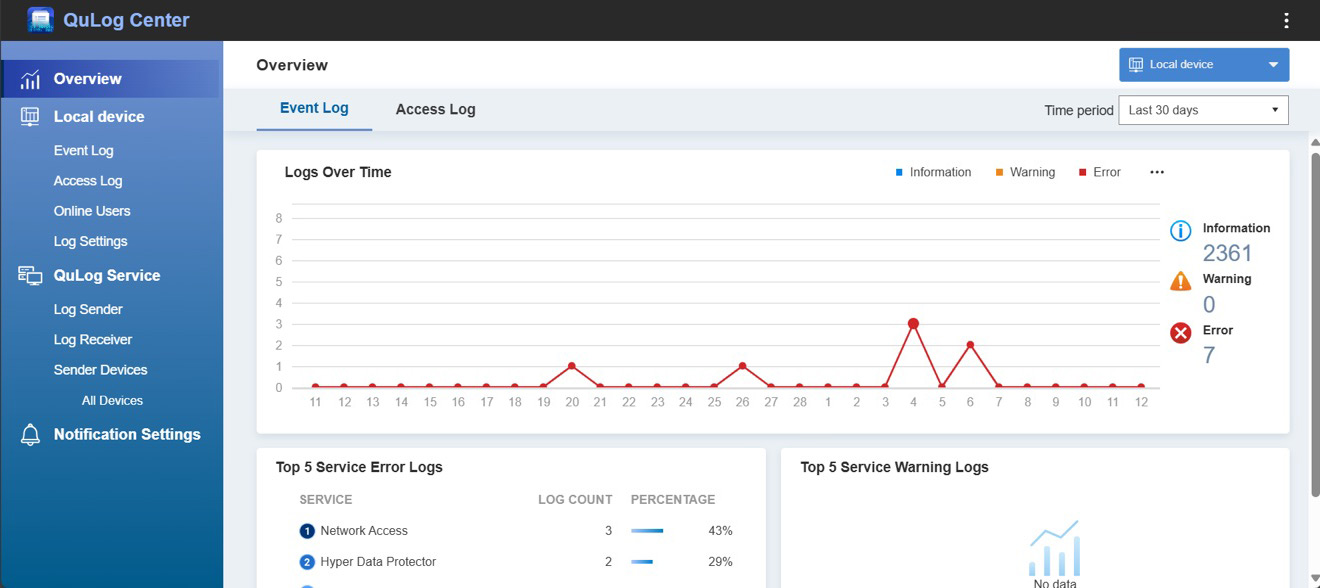
Audit evidence: User and group list, permission settings page audit, login records—QuLog Center filter and export CSV by period

A.5.3・A.5.18・A.8.2
Privileged Account Management
- Disable default admin, use named management accounts (strengthen basic steps)
- Separate administrator and general user accounts
- Delegated roles: system, application, backup, etc. each with their own permissions
- Administrative operations are logged in system event records
Audit evidence: Admin account list, account anomalies, and management operation event logs (QuLog Center export)

A.8.24・A.8.3・A.5.33
Data Protection
- volume AES-256 encryption, SED self-encrypting hard disk drives support
- Transmission encryption: HTTPS/TLS, SMB encryption, SFTP/FTPS
- WORM data folder and Immutable Snapshot QuTS hero only
- QuObjects Object Lock——S3-compatible immutable object storage
- HBS client-side encrypted backup
Audit evidence: Encryption status, WORM/snapshot retention settings page evidence

A.8.15–A.8.17
Logs and Monitoring
- QuLog Center centralized log management and retention
- Syslog forwarding——integration with enterprise SIEM (centralized security monitoring platform)
- NTP time synchronization, ensuring consistent time across devices (A.8.17)
- Abnormal login notifications, event alert rules
Audit evidence: Log retention and forwarding settings, alert history, SIEM query results

A.8.13–A.8.14
Backup and Recovery
- 3-2-1-1-0 backup principle—HBS 3 multi-destination backup and synchronization
- Snapshot and Snapshot Replica remote copy
- Immutable backup destination: WORM QuTS hero only, Object Lock
- Airgap+ isolated backup (requires QNAP networking equipment)
- data integrity check (hash comparison), includes report download
Audit evidence: Backup task results, integrity check report (downloadable), snapshot retention strategy

A.8.8·A.8.19·A.5.37
Vulnerabilities and Remediation
- PSIRT product security incident response, security advisories, and CVE public lookup
- QNAP Security Bounty Program vulnerability reward plan
- Firmware digital signature, automatic security patch update (scope configurable)
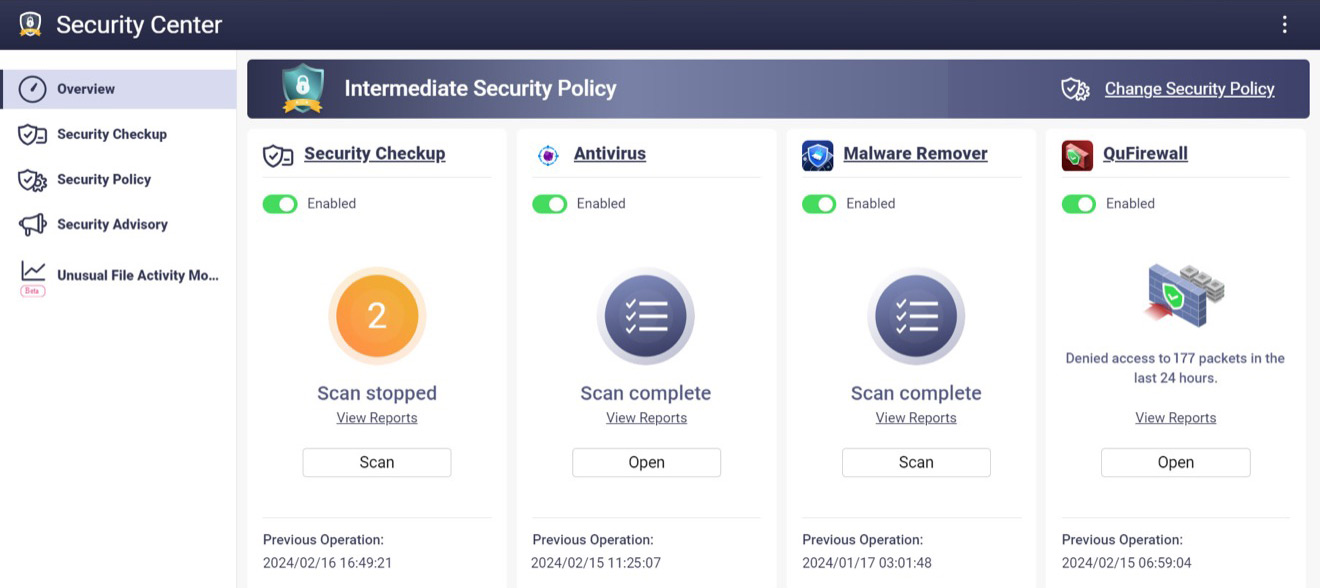
- Malware Remover and security risk scan
- Product support period (EOL/EOS) public inquiry
Audit evidence: Firmware version, security advisory mapping, update records, support period documents

A.8.20–A.8.22
Network Security
- SSH/Telnet and other unnecessary services are disabled by default
- QuFirewall Firewall: IP allow list, geo-blocking
- TLS certificate management, enforce HTTPS management connection
- Custom service port and source access restrictions
Audit evidence: Service and port settings, firewall rules, TLS settings page as proof

A.5.24–A.5.28・A.8.10 (handling)
Event Response and Handling
- QuLog log filtering and export, supports event investigation
- Snapshot rollback to the data state before being affected by restore
- Event notifications and forwarding log
- device retirement: Secure disk erase (Secure Erase)
Audit evidence: Event period log export, notification log, erase operation log
Note: The Annex A numbering corresponds to QNAP’s mapping to ISO/IEC 27002:2022 and is provided for reference during adoption; for formal applicability determination, please refer to your company’s risk assessment and the opinions of certification bodies.